Key Takeaways - NIST SP 800-53 R5 (High)
- NIST SP 800-53 R5 High baseline is the most comprehensive control set, including all Low, Moderate, and High-specific controls across 20 families.
- Required for systems where loss could cause severe or catastrophic adverse effects. Critical infrastructure, national security, defense systems.
- Supports CMMC Level 3 preparation. CMMC L3 requires NIST 800-172 (enhanced) on top of NIST 800-53 High.
- ComplianceForge offers four tiers from foundational policies to near-turnkey comprehensive documentation.
- All products are editable, customized with your logo, and delivered the same day.
Maximum ProtectionNIST SP 800-53 Rev 5 High Baseline Solutions
When you look at it from a sliding scale of good, better, great or awesome, we have a few options for you to meet your needs and budget to align your company with NIST 800-53. The product names you see in the various packages below map into the matrix shown above to show you how that maps into NIST 800-53.
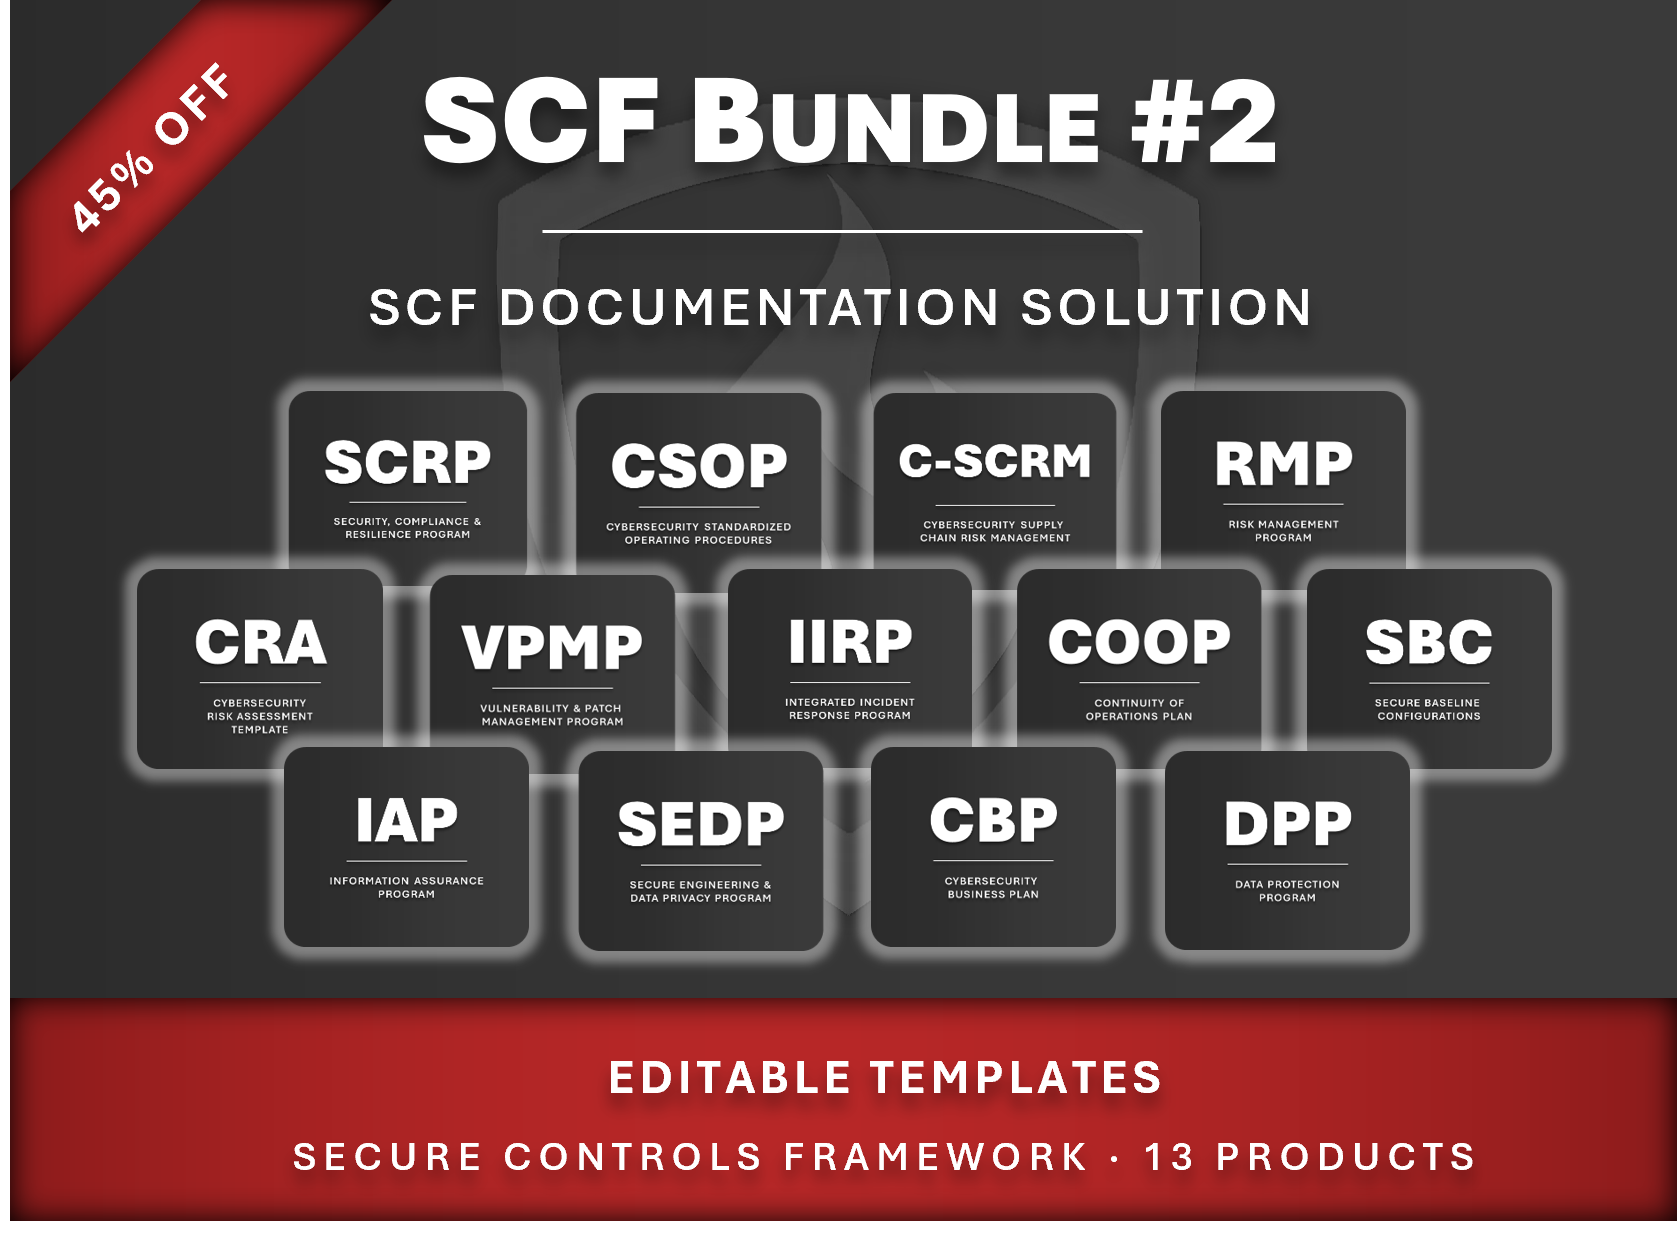
SCF Bundle 2 is the most comprehensive Secure Controls Framework (SCF) documentation set from ComplianceForge, with thirteen (13) coordinated products built on the Security, Compliance & Resilience Program (SCRP), which maps to 200+ laws, regulations & frameworks. Beyond the policies, standards and procedures, it covers risk management, risk assessments, vulnerability management, incident response, continuity of operations, secure configurations, information assurance, secure engineering, supply chain risk, data privacy and a cybersecurity business plan.
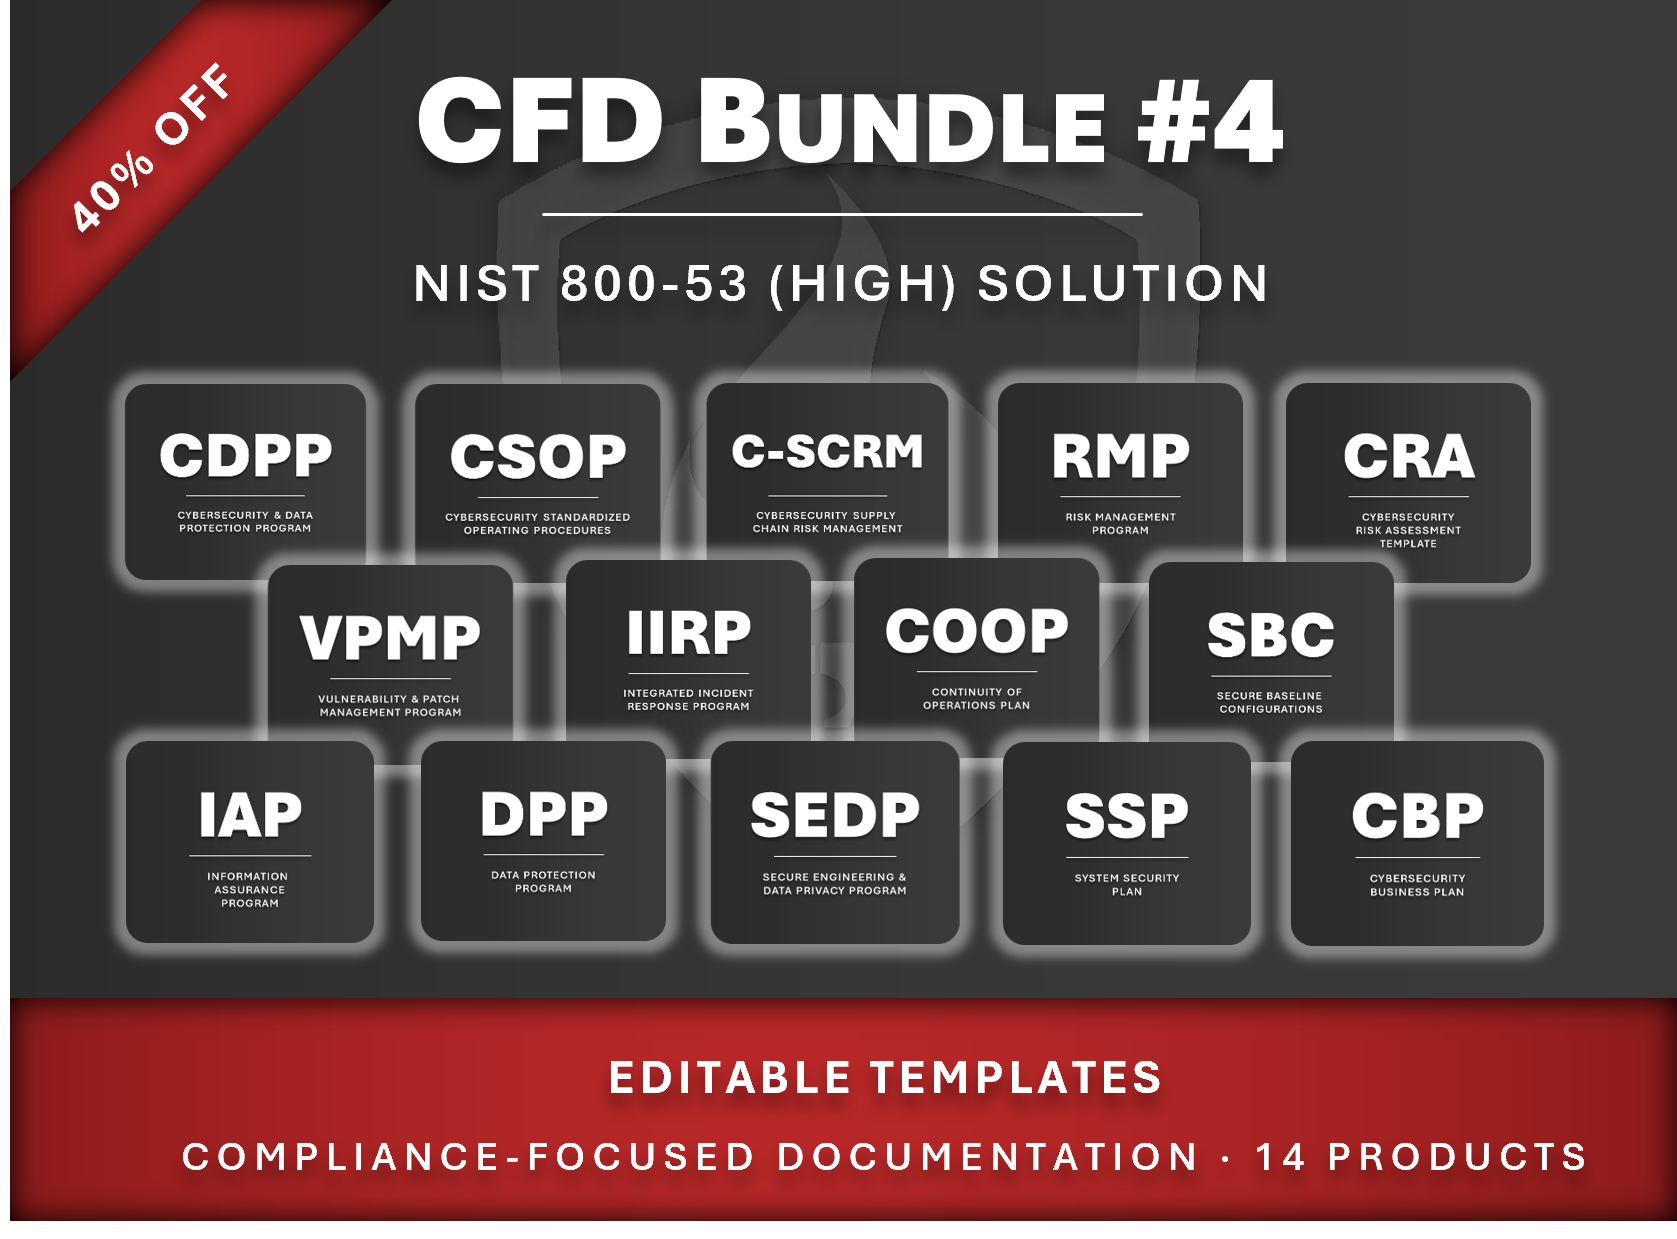
CFD Bundle 4 is the full-program NIST 800-53 R5 High documentation set from ComplianceForge, with fourteen (14) coordinated products. Beyond the policies, standards and procedures, it covers risk management, risk assessments, vulnerability management, incident response, continuity of operations, secure configurations, information assurance, secure engineering, supply chain risk, data privacy, a NIST 800-171 SSP template and a cybersecurity business plan, all built on the same framework.
PSP Bundle 4 is the most comprehensive PSP bundle from ComplianceForge, covering every NIST 800-53 R5 control across the Low, Moderate and High baselines, plus privacy controls. It is built for systems where a loss of confidentiality, integrity or availability would have a severe impact. It pairs our editable policies and standards (CDPP) with the matching procedures (CSOP), so what your organization requires and how your team carries it out are written to the same framework.
This version of the Cybersecurity Standardized Operating Procedures (CSOP) is based on the NIST 800-53 Rev 5 framework. It contains cybersecurity procedures that align with NIST 800-53 (including NIST 800-171 & CMMC requirements). You get fully-editable Microsoft Word documents that you can customize for your specific needs.
This version of the Cybersecurity & Data Protection Program (CDPP) is based on the NIST SP 800-53 rev5 framework. It contains cybersecurity policies and standards that align with NIST SP 800-53 (including NIST SP 800-171 requirements). You get fully-editable Microsoft Word and Excel documents that you can customize for your specific needs.
What problems Are There?What Problem Does ComplianceForge Solve?
Lack of In House Security Experience
Writing security documentation is a skill that many good cybersecurity professionals simple are not proficient at and avoid the task at all cost. Tasking your security analysts and engineers to write comprehensive documentation means you are actively taking them away from protecting and defending your network, which is not a wise use of their time. ComplianceForge offers cybersecurity documentation solutions that can save your organization significant time and money!
Audit Failures
Security documentation does not age gracefully like a fine wine. Outdated documentation leads to gaps that expose organizations to audit failures and system compromises. Our documentation provides mapping to leading security frameworks to show you exactly what is required to both stay secure and compliant. Being editable documentation, you are able to easily maintain it as your needs or technologies change.
Vendor Requirements
It is very common for clients and partners to request evidence of a security program and this includes policies and standards. Our documentation solutions provide this evidence!
How Does ComplianceForge Help?Clear Solution To Problems
Clear Documentation
ComplianceForge provides comprehensive documentation that can prove your security program exists. This equates to a time saving of hundreds of hours and tens of thousands of dollars in staff and consultant expenses!
Time Savings
Our cybersecurity documentation can provide your organization with a semi-customized solution that requires minimal resources to fine tune for your organization's specific needs.
Alignment With Leading Practices
Our documentation is mapped to NIST 800-53, as well as other leading security frameworks!
Common QuestionsFrequently Asked Questions (FAQs)
Here are answers to common questions about the NIST SP 800-53 high baseline:
When is the NIST 800-53 high baseline required?
The NIST 800-53 high baseline applies to high-impact systems, meaning at least one security objective (confidentiality, integrity or availability) is rated high. Under FIPS 199, high impact means a loss could have a severe or catastrophic adverse effect on organizational operations, organizational assets or individuals. FIPS 199 uses a high-water mark, so the highest impact value among the information types on a system sets its rating. Federal agencies must apply the matching baseline to those systems.
How many control families are in NIST SP 800-53 Rev 5?
NIST SP 800-53 Rev 5 has 20 control families. They are Access Control, Awareness and Training, Audit and Accountability, Assessment, Authorization and Monitoring, Configuration Management, Contingency Planning, Identification and Authentication, Incident Response, Maintenance, Media Protection, Physical and Environmental Protection, Planning, Program Management, Personnel Security, PII Processing and Transparency, Risk Assessment, System and Services Acquisition, System and Communications Protection, System and Information Integrity, and Supply Chain Risk Management.
What changed in NIST SP 800-53 Release 5.2.0?
Release 5.2.0, issued by NIST on August 27, 2025, focused on software development and deployment, including resiliency by design, developer testing, the deployment and management of updates, and software integrity and validation. It added SA-15(13), SA-24 and SI-02(07), revised SI-07(12) and updated discussion sections in existing controls. NIST made no changes to the control baselines, although SP 800-53B received a matching release for consistency.
Where can I download NIST SP 800-53 Rev 5?
NIST SP 800-53 Rev 5 is free to download as a PDF from the NIST Computer Security Resource Center (CSRC). The same page links to the current control catalog in the Cybersecurity and Privacy Reference Tool, machine-readable OSCAL versions in JSON, XML and YAML, a crosswalk to ISO/IEC 27001:2022 and mappings to the NIST Cybersecurity Framework. The low, moderate and high control baselines are published separately in NIST SP 800-53B.
Does ComplianceForge offer NIST 800-53 high baseline policies?
Yes, ComplianceForge offers editable policies and standards aligned with the NIST SP 800-53 Rev 5 high baseline, and they also include NIST SP 800-171 requirements. If you need procedures, PSP Bundle 4: NIST 800-53 R5 (High) adds them, and CFD Bundle 4: NIST 800-53 (High) includes 14 products for operationalizing the control set. You can edit any of our products and brand them with your company logo, and we deliver them the same day.