- Vulnerability management is one of the most frequently cited areas in audit findings and breach post-mortems.
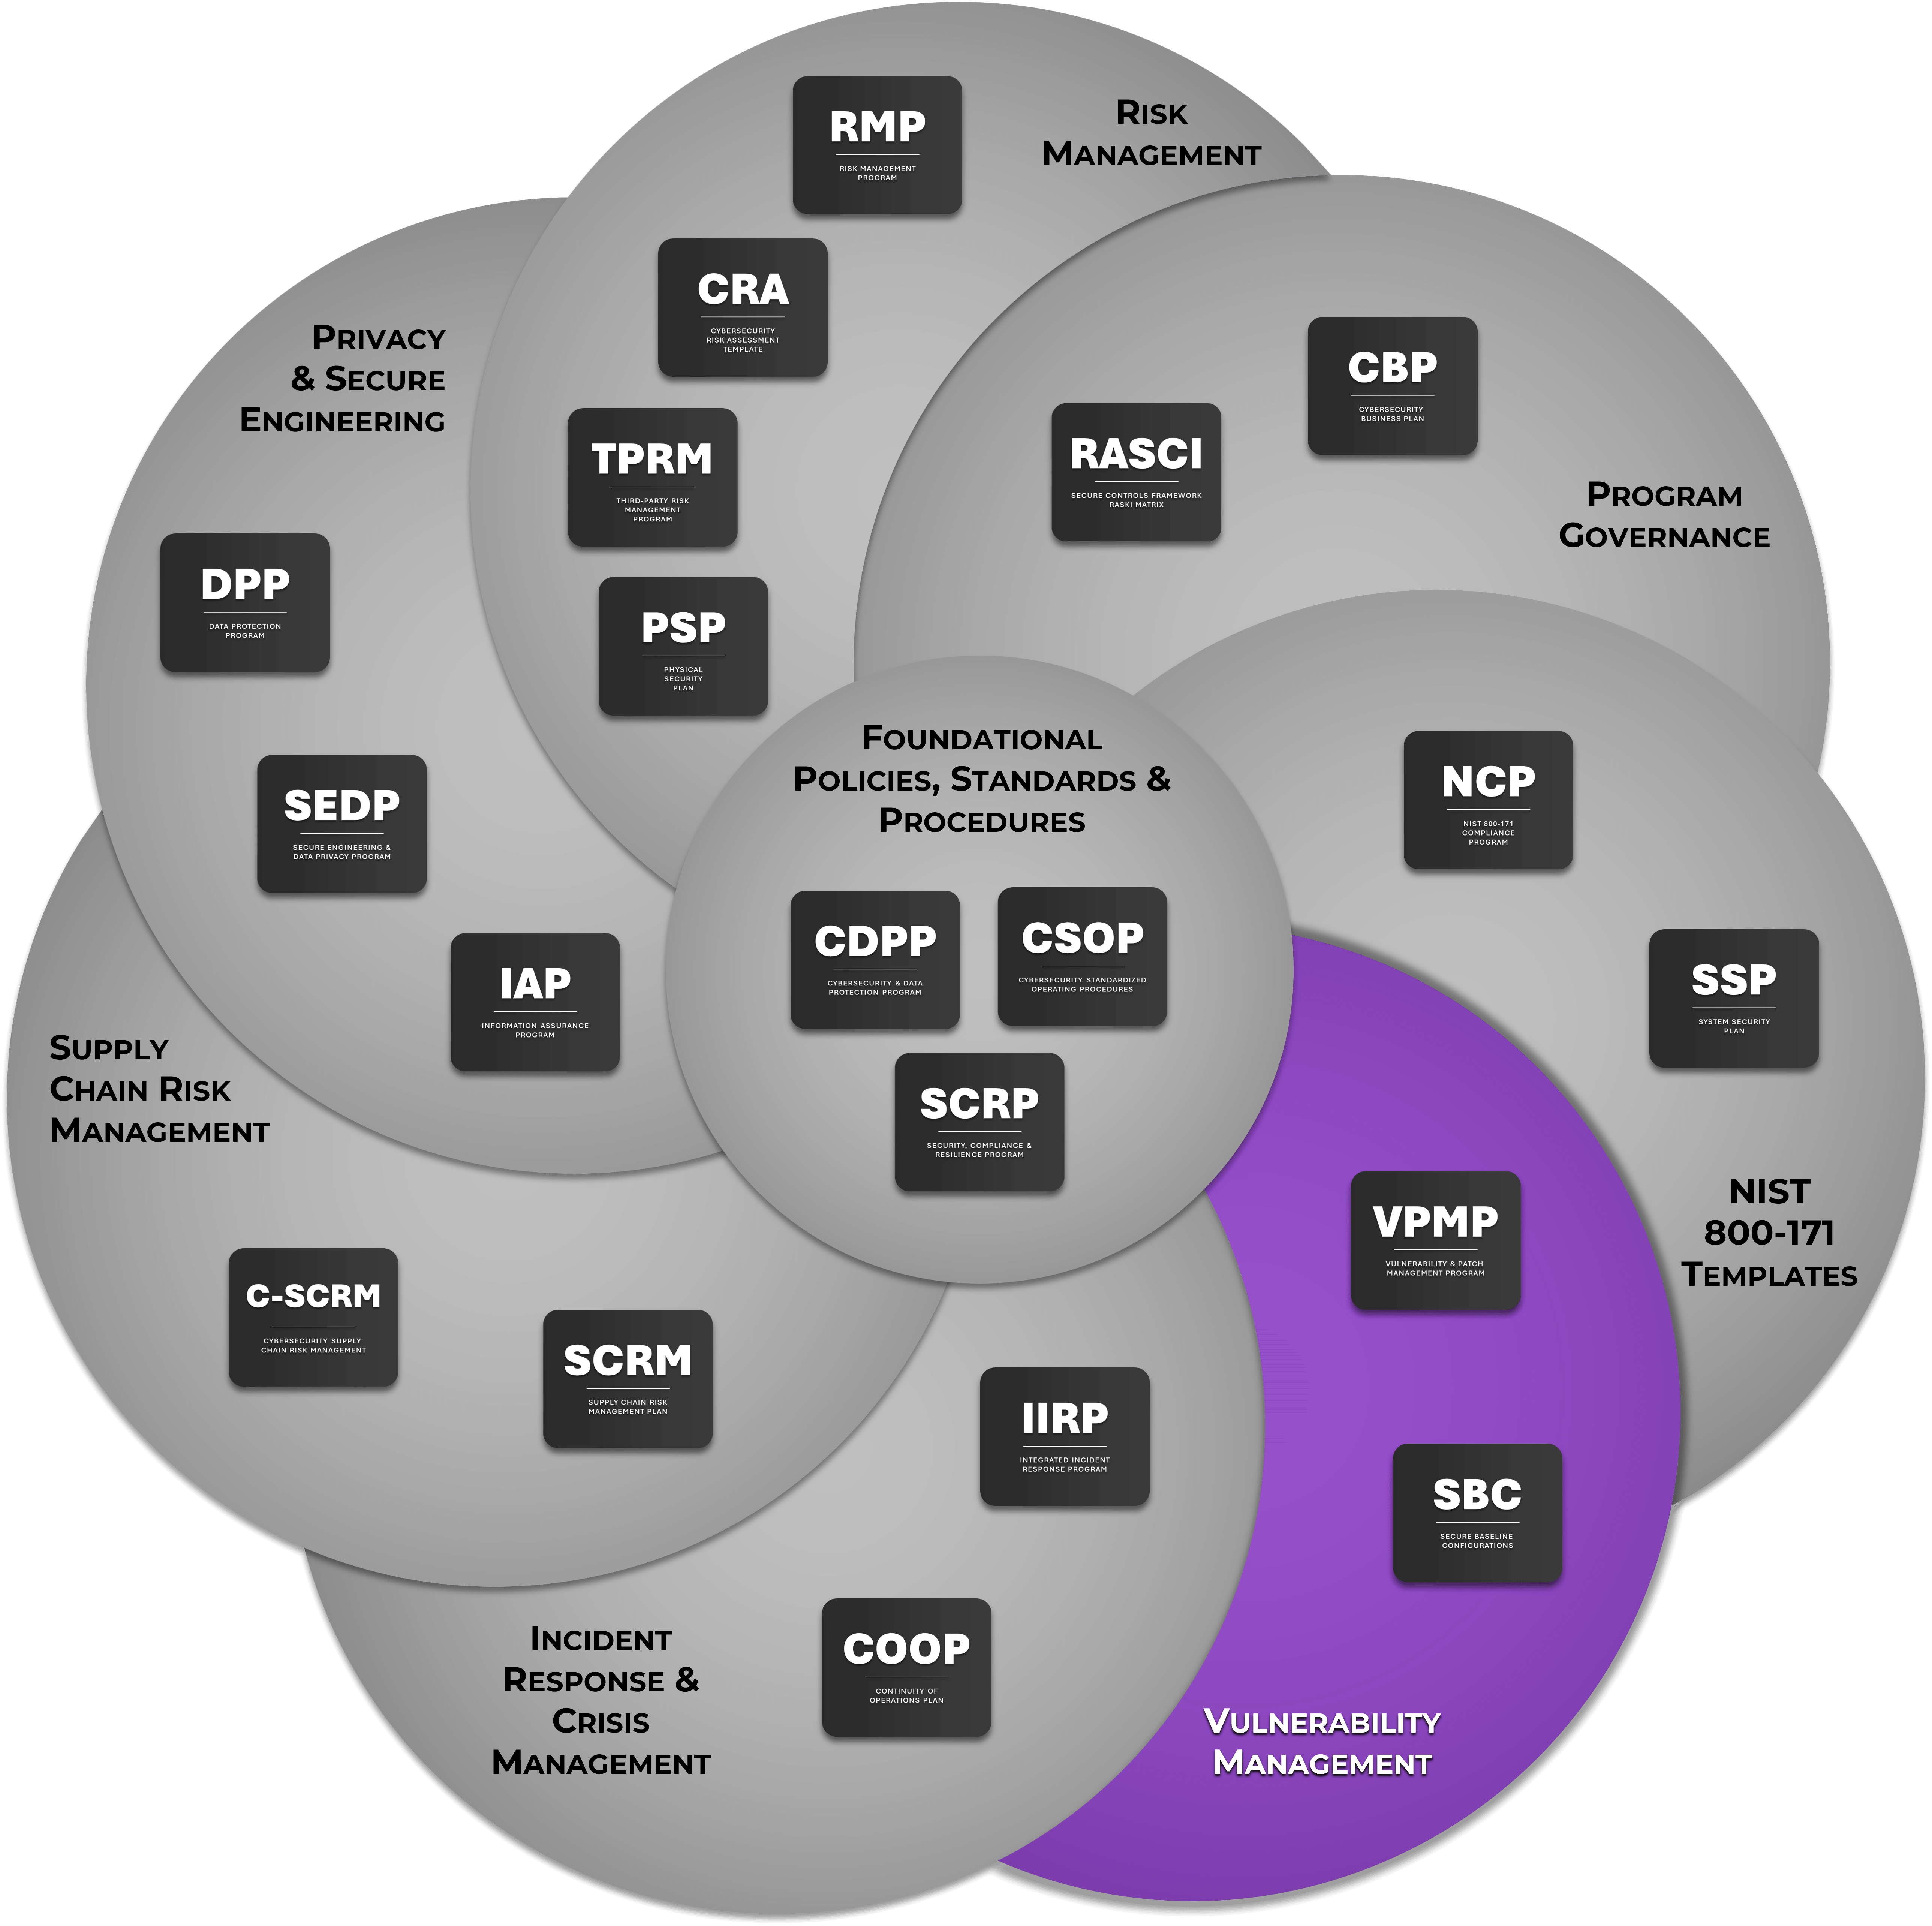
- Two focused products: VPMP (Vulnerability & Patch Management Program) and SBC (Secure Baseline Configurations).
- The VPMP documents the operational workflow: scanning, prioritization, patching, exception handling, and executive reporting.
- The SBC documents hardening baselines for operating systems, applications, network devices, and cloud infrastructure.
- Together the two products address the two sides of vulnerability management: the "what" of hardened baselines and the "how" of ongoing operations.
Vulnerability Management & Hardening Documentation
When you "peel back the onion" and prepare for an audit, there is a need to address "the how" for certain topics, such as vulnerability management. While policies and standards are designed to describe WHY something is required and WHAT needs to be done, many companies fail to create documentation to address HOW the policies and standards are actually implemented. We did the heavy lifting and created several program-level documents to address this need and the Vulnerability & Patch Management (VPMP) is one of those products.
The two products in this category address the two sides of vulnerability management. The Vulnerability & Patch Management Program (VPMP) documents the operational workflow for discovering, prioritizing, and remediating vulnerabilities across the environment. The Secure Baseline Configurations (SBC) documents the hardening standards that prevent vulnerabilities from being introduced in the first place by ensuring all systems are deployed with security-appropriate configurations.
Most mature organizations maintain both. The VPMP without hardening baselines results in an endless remediation treadmill. Hardening baselines without the VPMP result in gradual drift as systems evolve. Together, they provide end-to-end vulnerability management coverage.
Vulnerability Management Is An Audit Hot Spot
Vulnerability management is one of the most frequently audited security domains across every major framework. PCI DSS requires specific vulnerability scanning cadences. HIPAA expects vulnerability management as part of risk analysis. CMMC Level 2 has explicit vulnerability management practices. NIST 800-53 has dedicated control families for vulnerability and configuration management.
Undocumented or inadequately documented vulnerability management is consistently one of the top audit findings. The VPMP and SBC address this risk directly with structured, defensible documentation.
Available Vulnerability Management Products
Two complementary products covering different aspects of vulnerability management. Purchase individually or combine for full coverage.
Comprehensive Coverage
Give us a call or send us an email - we are happy to help you find the right solution for your needs!
There are a lot of choices to pick from when selecting a cybersecurity framework. If you are not sure what works best for you, you can read more here. The most common frameworks are NIST 800-53, ISO 27002, the NIST Cybersecurity Framework and the Secure Controls Framework (SCF). To do NIST CSF, ISO 27002 or NIST SP 800-53 properly, it takes more than just a set of policies and standards. While those are foundational to building a cybersecurity program aligned with that framework, there is a need for program-specific guidance that helps operationalize those policies and standards (e.g., risk management program, third-party management, vulnerability management, etc.). It is important to understand what is required to comply with NIST CSF vs ISO 27002 vs NIST SP 800-53, since there are significantly different levels of expectation.
It is important to understand that picking a cybersecurity framework is more of a business decision and less of a technical decision. Realistically, the process of selecting a cybersecurity framework must be driven by a fundamental understanding of what your organization needs to comply with from a statutory, regulatory and contractual perspective, since that understanding establishes the minimum set of requirements necessary to:
- Not be considered negligent with reasonable expectations for cybersecurity & data protection;
- Comply with applicable laws, regulations and contractual obligations; and
- Implement the proper controls to secure your systems, applications and processes from reasonable threats, based on your specific business case and industry practices.
This understanding makes it easy to determine where on the "framework spectrum" (shown above) you need to focus for selecting a set of cybersecurity principles to follow. This process generally leads to selecting the NIST Cybersecurity Framework, ISO 27002, NIST SP 800-53 or SCF as a starting point.
Frequently Asked Questions (FAQs)
Here are answers to common questions about vulnerability and patch management: