Quality, Expert-Derived Cybersecurity Documentation To Keep Organizations Secure, Compliant & Resilient  |  Got Questions? +1-307-241-8740
ComplianceForge

NIST 800-171 & CMMC - Where Do I Start?

Meticulous documentation is the unsung hero in ensuring compliance with NIST 800-171 and readiness for a CMMC assessment. ComplianceForge makes NIST 800-171 compliance as easy and affordable as possible with editable policies, standards, procedures, SSP/POA&M templates, and more.

Key Takeaways - NIST 800-171 & CMMC - Where Do I Start?
  • ComplianceForge offers 4 main paths for CMMC / NIST 800-171 compliance. The right one depends on whether you only need CMMC or have broader compliance obligations.
  • The NCP (NIST 800-171 Compliance Program) is the easy button for organizations that only need CMMC Level 2 / NIST 800-171 compliance, the most cost-effective and efficient choice.
  • If you need to speak NIST 800-53 for other contracts (FedRAMP, RMF, FISMA), consider Bundle #2 (moderate baseline) or Bundle #3 (high baseline).
  • For enterprise-class environments with multiple compliance needs, Bundle #4 leverages the SCF for 200+ framework coverage.
  • ComplianceForge documentation is already updated for NIST 800-171 R3. NCP includes one year of updates.
Select The Right Solution

Choose Your Compliance Path

Meticulous documentation is the unsung hero in ensuring your organization's compliance with NIST 800-171 and readiness for a CMMC assessment. ComplianceForge is here to help make NIST 800-171 compliance as easy and as affordable as possible. We specialize in compliance-related documentation solutions (e.g., policies, standards, procedures, SSP/POA&M templates, SCRM Plans, etc.). ComplianceForge offers quite a few options for CMMC / NIST 800-171 compliance efforts. It really depends on the focus of your compliance efforts, since the right solution depends on if you just need to comply with CMMC / NIST 800-171 or if you have other compliance obligations that you need to address:
$ 3,000.00 USD
CMMC Bundle 1: Level 1 (CMMC 2.0 L1 & FAR 52.204-21)
The CMMC Level 1 Bundle includes two (2) ComplianceForge products for those needing to demonstrate compliance with Cybersecurity Maturity Model Certification (CMMC) Level 1.
Contains:
Word
Excel
PowerPoint
PDF
Examples:
Word Example
Excel Example
See Individual Products
$ 10,530.00 USD
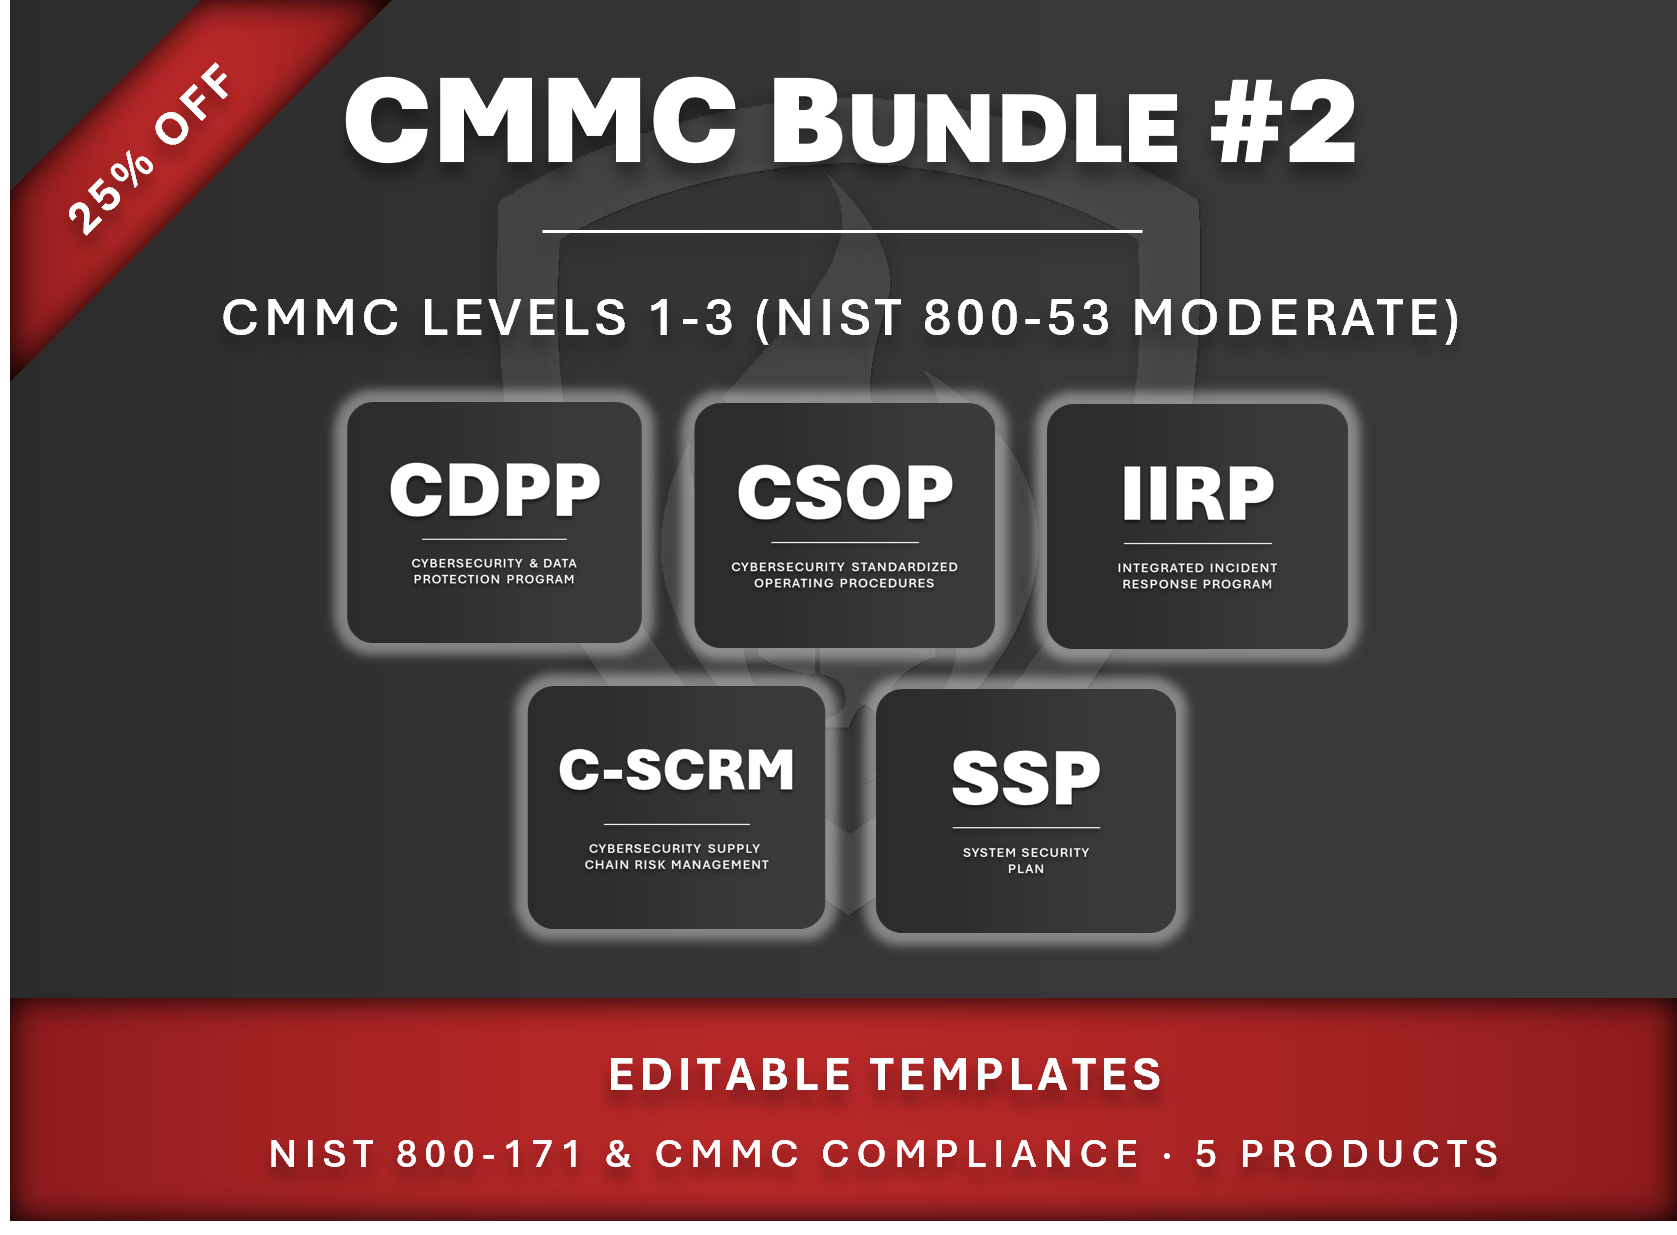
CMMC Bundle 2: Levels 1-2 (NIST 800-53 Moderate)
This is a bundle that includes five (5) ComplianceForge products that are focused on operationalizing NIST SP 800-53 R5 (low & moderate baselines).
$ 5,200.00 USD
NIST 800-171 Compliance Program (NCP)
The NCP is designed to fit the needs of small to medium businesses in need of a “square peg for a square hole” to singularly address NIST 800-171 and CMMC compliance requirements. The NCP is "battle tested" - our clients have successfully passed DIBCAC assessments with this documentation, including a CMMC Third-Party Assessment Organization (C3PAO).
Included Products:
No items found.
Contains:
Word
Excel
PowerPoint
PDF
Examples:
Word Example
Excel Example
See Individual Products
Enforcement Is Active

CMMC 2.0 Implementation Timeline

The Department of Defense activated Phase 1 of CMMC 2.0 on November 10, 2025. Compliance is no longer voluntary and is now a mandatory requirement for winning and retaining DoD contracts.

Phase
Timeline
Requirement
Phase 1
Nov 2025 – Nov 2026
Self-assessments for Level 1 and Level 2. CMMC requirements appear in new solicitations.
Phase 2
Nov 2026 – Nov 2027
Mandatory C3PAO third-party assessments required for most Level 2 contracts.
Phase 3
Nov 2027+
Full CMMC enforcement. All contractors must hold valid certifications at the required level.
How Long Does It Take To Become CMMC Compliant?

For an average company, Level 2 implementation takes 12 to 24 months and C3PAO assessment backlogs are running anywhere from 2 to 10 months (depending on the reputational quality of the C3PAO). Organizations that haven't started are already behind the Phase 2 deadline. ComplianceForge's NCP can significantly accelerate the documentation portion of your compliance journey.

Significant Changes Between R2 & R3

Planning For NIST 800-171 Rev 3

There are significant changes between NIST 800-171 R2 and R3. ComplianceForge documentation is already updated for Rev 3 to make your transition as smooth as possible.

NIST 800-171 R3 policies, standards and procedures poster
Unified Scoping Guide

Scoping Guide For NIST 800-171 & CMMC

Arguably, determining what is and is not in scope for NIST 800-171 and CMMC is one of the most difficult steps in your compliance journey.

The Unified Scoping Guide (USG) is a free resource that is intended to help organizations define the scope of the sensitive data where it is stored, transmitted and/or processed. This guide will refer to both sensitive and regulated data as “sensitive data” to simplify the concept this document is focused on. This model categorizes system components according to several factors:

  • Whether sensitive data is being stored, processed or transmitted;
  • The functionality that the system component provides (e.g. access control, logging, antimalware, etc.); and
  • The connectivity between the system and the sensitive data environment.

This is an evolution of the CUI Scoping Guide that ComplianceForge previously published. This new version is updated to reflect the DoD's CMMC 2.0 Level 2 Scoping Guidance that includes Controlled Unclassified Information (CUI) scoping considerations, but expands on the model to address a broader category of sensitive and regulated data. This document can be used to help companies define what is in scope to comply with NIST SP 800-171 and appropriately prepare for a CMMC assessment, since a significant step towards becoming NIST SP 800-171 compliant and being able to pass a CMMC assessment is understanding the scope of the CUI environment.

The Unified Scoping Guide (USG) is intended to help organizations define the scope of the sensitive data where it is stored, transmitted and/or processed. This guide will refer to both sensitive and regulated data as “sensitive data” to simplify the concept this document is focused on. This approach is applicable to the following sensitive data types:

  • Controlled Unclassified Information (CUI)
  • Personally Identifiable Information (PII)
  • Cardholder Data (CHD)
  • Attorney-Client Privilege Information (ACPI)
  • Export-Controlled Data (ITAR / EAR)
  • Federal Contract Information (FCI)
  • Protected Health Information (PHI)
  • Intellectual Property (IP)
  • Student Educational Records (FERPA)
  • Critical Infrastructure Information (CII)
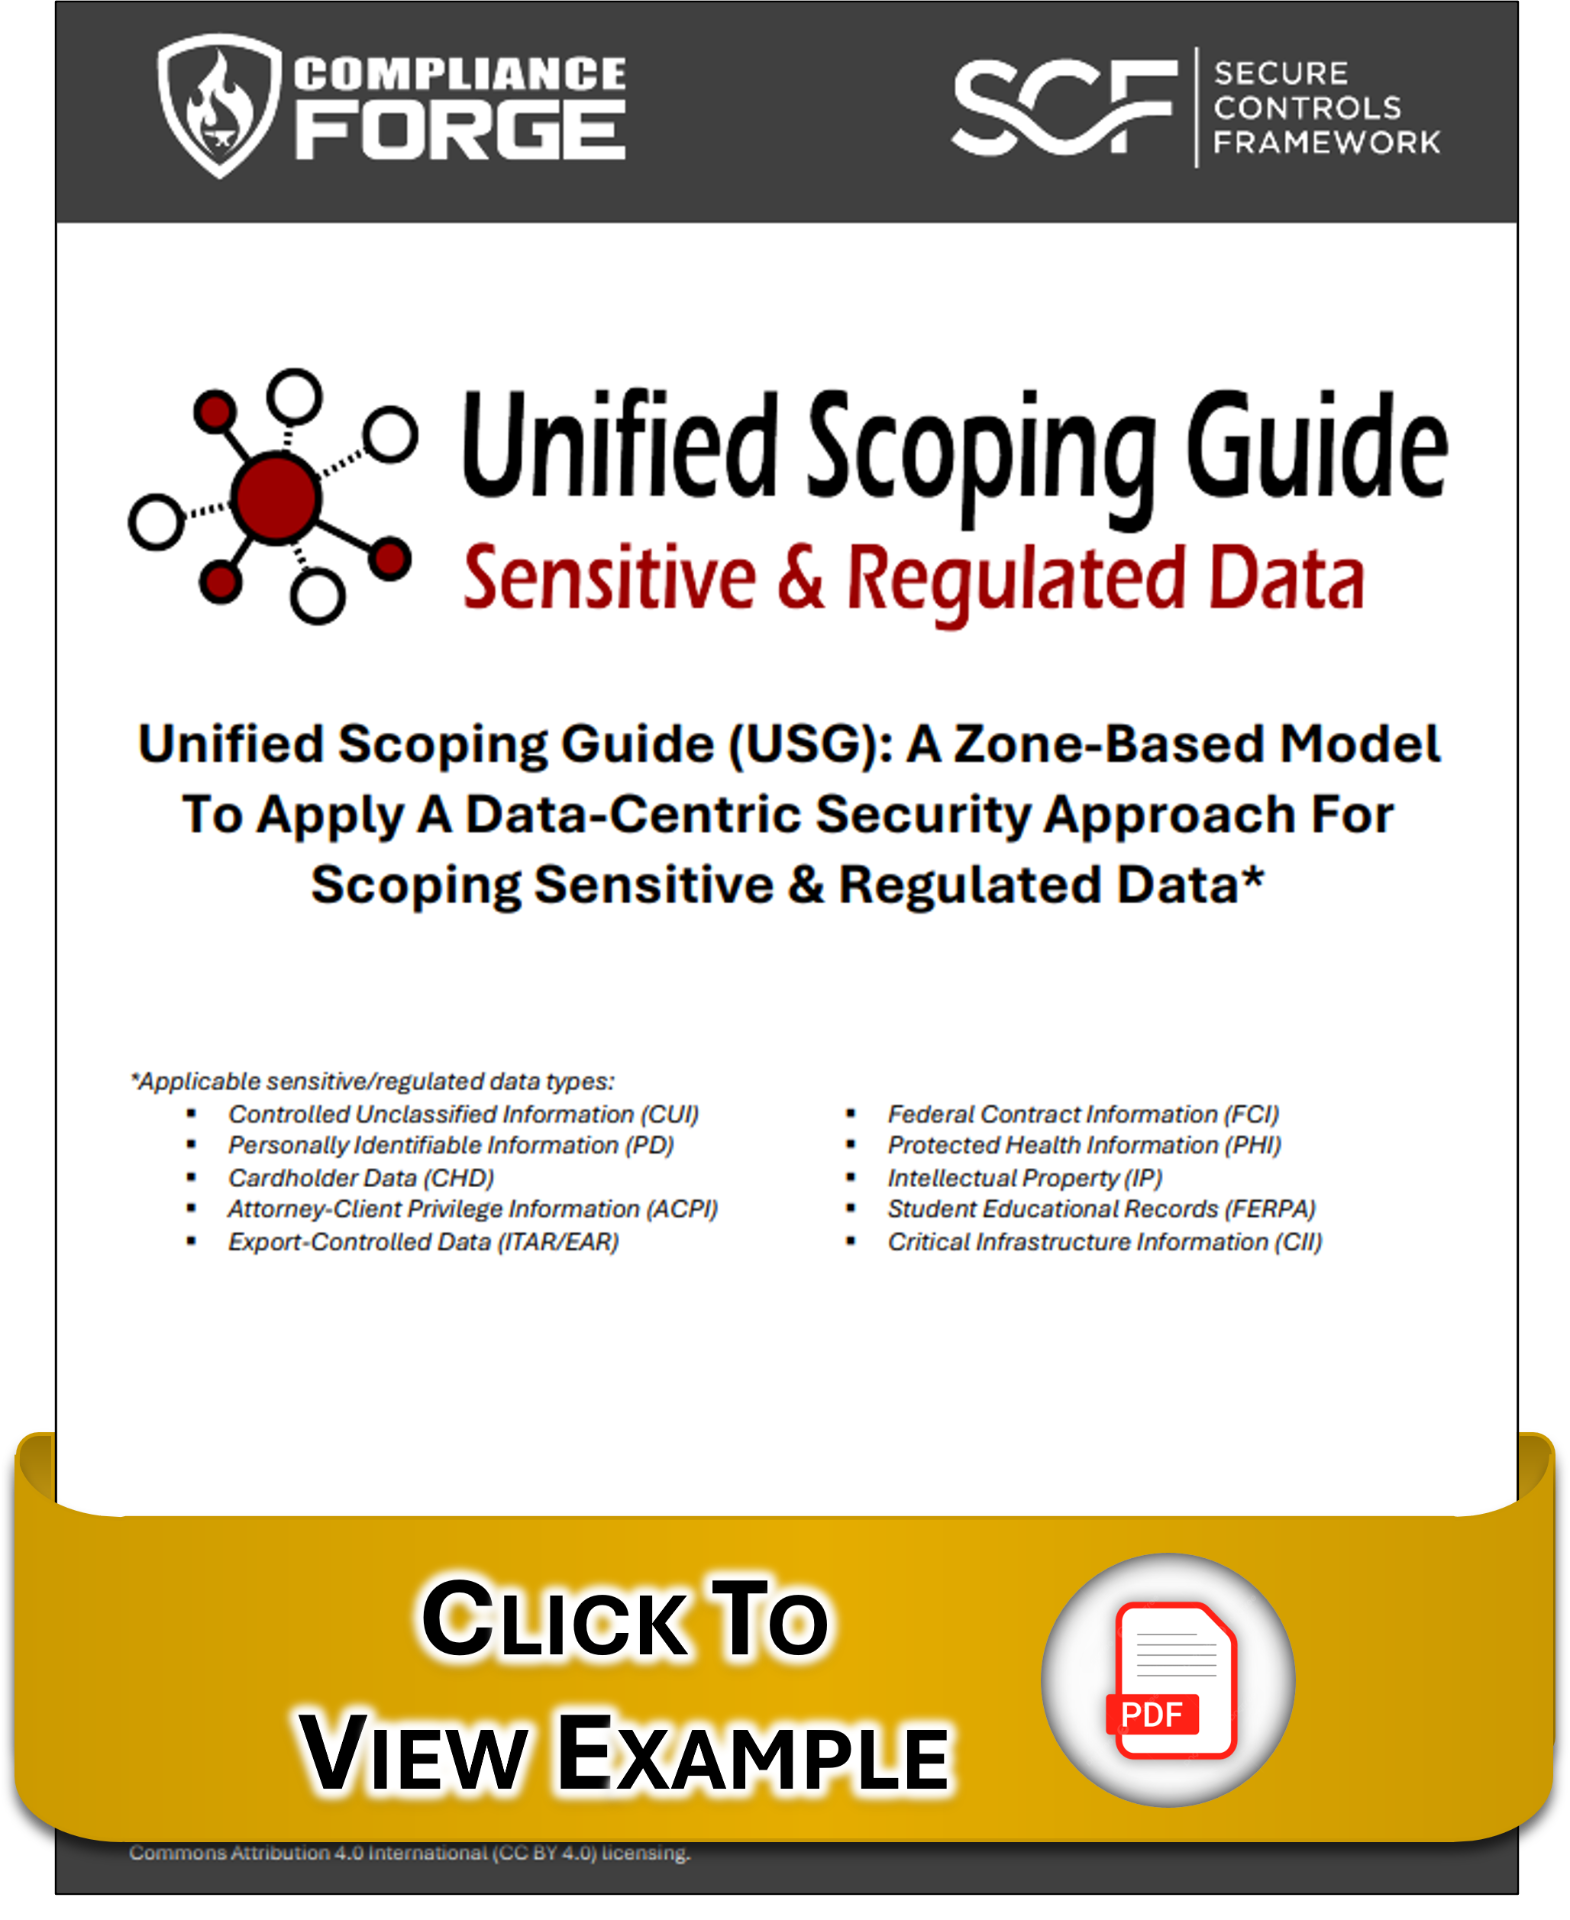
Cover USG Unified Scoping Guide
Common Questions

Frequently-Asked Questions

Here are answers to the questions defense contractors ask most when getting started:

Where should a defense contractor start with NIST 800-171 and CMMC?
Start by confirming what type of federal data your contracts involve and where that data lives. Contracts involving Federal Contract Information (FCI) carry FAR 52.204-21, while contracts involving Controlled Unclassified Information (CUI) typically carry DFARS 252.204-7012, which requires NIST SP 800-171. Once you know the data type, define the scope of the people, systems and facilities that store, process or transmit it, since scope drives cost and effort. To help you categorize system components, ComplianceForge offers a free Unified Scoping Guide (USG).
Do I need CMMC Level 1 or Level 2?
The level depends on the data you handle. CMMC Level 1 applies when a contractor handles only FCI and covers the 15 basic safeguarding requirements in FAR 52.204-21, with an annual self-assessment and affirmation. CMMC Level 2 generally applies when CUI is involved and covers the 110 requirements of NIST SP 800-171 Rev 2. While CMMC remains in Phase 1, the DoD CIO describes Level 2 as a self-assessment every three years with annual affirmations.
How long does it take to prepare for CMMC Level 2?
Implementing CMMC Level 2 typically takes 12 to 24 months. The range depends on the size of your CUI scope, how mature your existing controls and documentation are, and how many of the 110 NIST SP 800-171 Rev 2 requirements still need work. Scoping first helps, since a smaller CUI environment means fewer systems to secure. The July 2026 suspension of CMMC Phase II did not change DFARS 252.204-7012, so if you handle CUI, you're still expected to implement NIST SP 800-171 now.
Should I buy the NCP or a CMMC bundle from ComplianceForge?
If NIST 800-171 and CMMC Level 2 are your only obligations, ComplianceForge recommends the NIST 800-171 Compliance Program (NCP), since it's the most cost-effective choice. If you also need NIST SP 800-53 language for FedRAMP, RMF or FISMA work, consider CMMC Bundle #2 (moderate baseline) or Bundle #3 (high baseline). For enterprise environments with many compliance obligations, take a look at Bundle #4, which is built on the Secure Controls Framework (SCF). Bundle #1 is aimed at CMMC Level 1 and FAR 52.204-21.
What documents are required for a CMMC Level 2 assessment?
The System Security Plan (SSP) is the core document, and 32 CFR 170.21 does not allow the SSP requirement to be placed on a Plan of Action & Milestones (POA&M), so it must be complete at assessment time. A POA&M records any requirements that are not yet met, within the limits the rule sets for Conditional status. Assessors also look for policies, standards and procedures that show how each requirement is performed, along with evidence that those practices actually operate.