
Key Takeaways - HIPAA Security Rule Certification
- The SCF partnered with The Cyber AB to create a legitimate HIPAA Security Rule certification path.
- Assessment uses NIST SP 800-66 Rev 2 as the reference for HIPAA Security Rule conformity.
- An SCR 3PAO certifies your organization as SCR Certified, HIPAA Security Rule through a conformity assessment.
- Ideal for Covered Entities, Business Associates and their service providers needing to prove HIPAA compliance.
- ComplianceForge provides gap assessment services and documentation to prepare for certification.
- StrikePath serves as recommended 3PAO partner with expertise in ComplianceForge documentation.
Beyond Self-Attestation
Why Get HIPAA Certified?
While the US Department of Health and Human Services (HHS) does not offer a formal certification program for the Health Insurance Portability and Accountability Act (HIPAA), there is a legitimate way to obtain a HIPAA Security Rule certification for Covered Entities (CE) and Business Associates (BA).
The Secure Controls Framework (SCF) partnered with The Cyber AB to be the Accreditation Body (AB) for the Secure, Compliant & Resilient Conformity Assessment Program (SCR CAP). This enables organizations to offer a certification path for the HIPAA Security Rule where an SCR Third-Party Assessment Organization (3PAO) can certify an entity as SCR Certified - HIPAA Security Rule through a conformity assessment useing SCF controls.
Note
The SCR CAP is focused on using the SCF as the control set to provide a company-level certification. While the SCR CAP shares some similarities with other existing, single-focused certifications (e.g., ISO 27001, CMMC, FedRAMP, etc.), the SCR CAP is unique in its metaframework approach to covering cybersecurity and data protection requirements that span multiple laws, regulations and frameworks.
The Path
Your Path To Demonstrating Conformity With HIPAA
If you want to get SCR Certified for the HIPAA Security Rule, you can download the HIPAA Security Rule (NIST SP 800-66) Assessment Guide from the SCF's website.
For organizations that have a current Cybersecurity Maturity Model Certification (CMMC) Level 2 certification and want to leverage reciprocity towards HIPAA Security Rule certification. (Note - this is only applicable if the organization holds a current CMMC L2 certification)
What Is The SCR CAP?
Secure, Compliant & Resilient Conformity Assessment Program (SCR CAP) - HIPAA Certification
The SCR CAP is designed for cybersecurity & privacy practitioners by cybersecurity & data privacy practitioners. This concept is based on the need within the industry for a tailored conformity assessment solution that is capable of addressing several key considerations:
- View compliance as a natural by-product of secure practices;
- Scale to address multifaceted operational requirements (e.g., laws, regulations and frameworks);
- Acknowledge the stated risk tolerance of the OSC since not all organizations have the same risk tolerance;
- Minimize the risk of “gaming” the certification process that provides no useful insights into the security posture of the OSA;
- Utilize technology to make the assessment process more efficient to drive down labor-related assessment costs; and
- Leverage existing industry recognized practices, where possible.
Enables Certification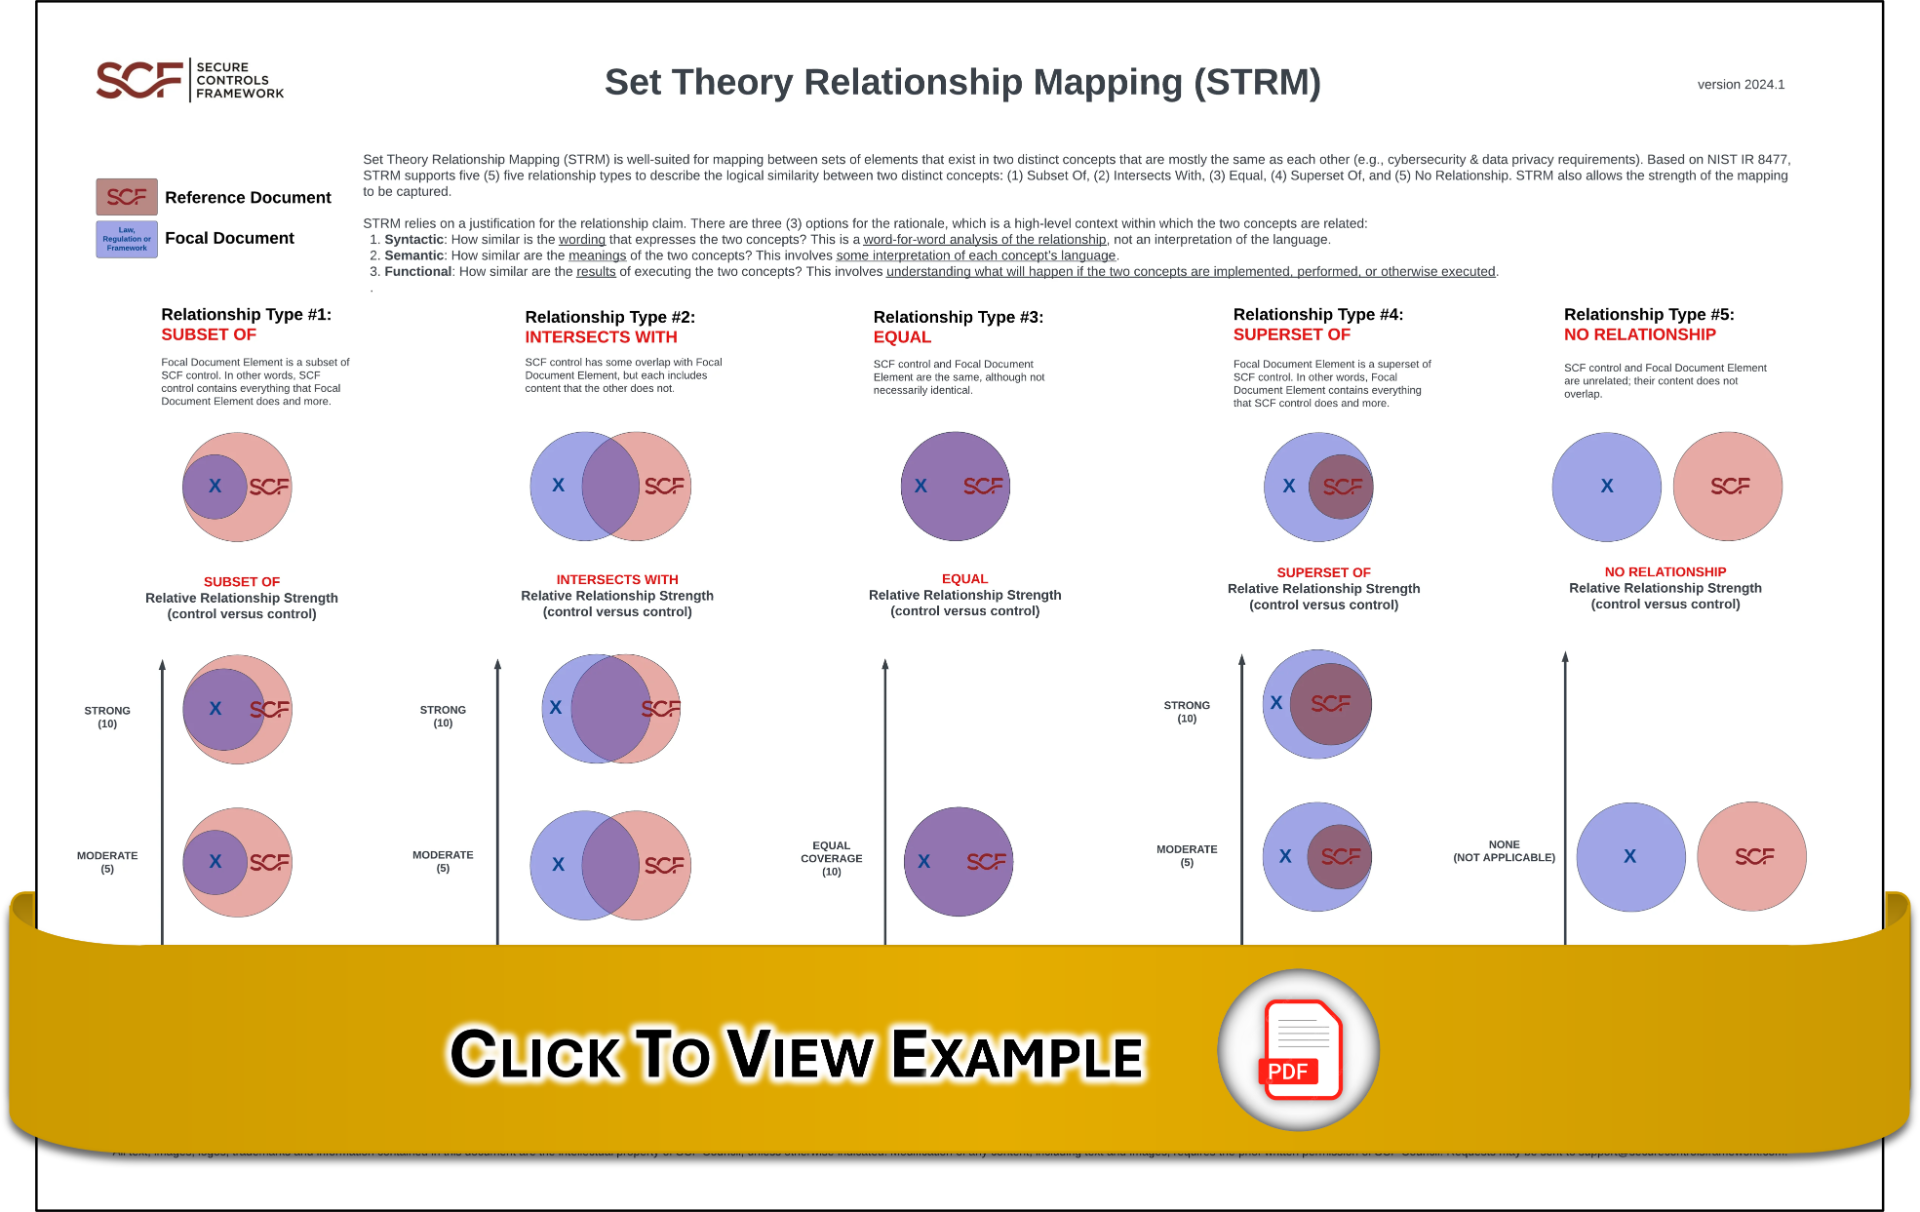
HIPAA Security Rule Structure Enables Certification
The lack of controls within HIPAA makes it difficult for organizations to demonstrate conformity with the framework. The solution is to leverage a controls framework that provides coverage for the HIPAA Security Rule and the SCF is that solution!
A HIPAA Security Rule-specific Assessment Guide (AG) is published for Organizations Seeking Assessment (OSA) to understand the assessment process. In addition to the SCR CAP’s assessment standards, the SCR CAP’s HIPAA Security Rule AG contains:
Additionally, the SCF has comprehensive controls coverage for NIST CSF 2.0. In adherence to NIST IR 8477, the SCF utilizes Set Theory Relationship Mapping (STRM) to provide crosswalk mapping between HIPAA Security Rule requirements to SCF controls. The result is a defendable set of controls and Assessment Objectives (AOs) that can be assessed against to demonstrate conformity with the HIPAA Security Rule.
What Is THe Certification Process?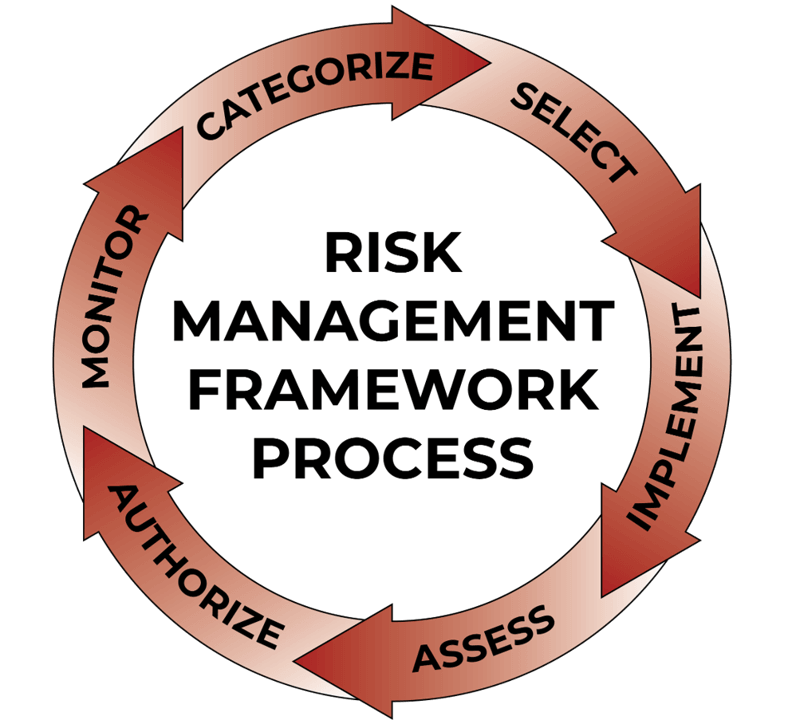
SCR Certification Process For The HIPAA Security Rule / NIST SP 800-66 Rev 2
The SCR CAP is designed to look at a holistic approach to cybersecurity and data protection. SCR assessors will evaluate your HIPAA Security Rule-specific approach to:
- Categorizing controls
- Selecting controls
- Implementing controls
- Assessing controls
- Authorizing controls
- Monitoring Controls
Where To Start?
HIPAA Security Rule Certification Starts With ComplianceForge!
To obtain HIPAA Securty Rule certification, these are the recommended steps:
- Contact ComplianceForge so that we can help you on your journey to demonstrate conformity with the HIPAA Security Rule;
- Download the HIPAA Security Rule assessment guide and familiarize yourself with the SCR CAP process;
- Implement the necessary controls to demonstrate conformity;
- Perform an internal assessment to validate assumptions and necessary evidence; and
- Engage an SCR 3PAO to conduct a third-party conformity assessment.
ComplianceForge can help you step-by-step through this process from start to finish. We want you to be success to obtain a HIPAA Security Rule certification!
Where To Get An Assessment?
HIPAA Security Rule Assessments
ComplianceForge can provide gap assessment services to provide independent assurance of your cybersecurity program to determine how it conforms with the HIPAA Security Rule (NIST SP 800-66 Rev 2).
The SCR CAP is an authoritative structure to conduct Third Party Assessment, Attestation and Certification Services (3PAAC Services). The SCR CAP is a scalable, cost-effective solution for organizations to obtain an independent, third-party assessment of its cybersecurity & data protection practices.
The SCR CAP is specifically designed to be:
- An affordable solution for businesses to obtain certification of its cybersecurity and data protection capabilities.
- Scalable to address the modern reality facing businesses for multiple compliance obligations.
- Sustainable by businesses to minimize the reliance upon expensive consultants.
The SCF-based certification for the HIPAA Security Rule is designed to deliver significant value through an efficient third-party assessment process. The SCR CAP employs a rigorous third-party assessment process governed by The Cyber AB. This governance ensures SCR Third-Party Assessment Organizations (SCR 3PAOs) implement the highest level of assurance in certification results, reinforcing trust and credibility with stakeholders. The assessment process is prescriptive and the results are unbiased.
Successfully demonstrating conformity with the HIPAA Security Rule will lead to an SCR Certified - HIPAA Security Rule certification!
StrikePath – Your NIST CSF Audit Partner
ComplianceForge has a strong working relationship with StrikePath to serve as your 3PAO for a HIPAA Security Rule assessment. StrikePath has expertise with ComplianceForge documentation and that can lead to a more efficient and cost-effective assessment process. Contact StrikePath to get on their calendar for your assessment!
What Solutions Does ComplianceForge Provide?
NIST CSF 2.0 Policies, Standards & Procedures
ComplianceForge has editable policies, standards and procedures for HIPAA / HITECH to assist your organization earning a HIPAA Security Rule certification as part of the SCR CAP:
$ 10,400.00 USD
Policies & Standards - Security, Compliance & Resilience Program (SCRP)
This version of the SCRP is a hybrid, "best in class" approach to cybersecurity documentation that covers dozens of statutory, regulatory and contractual frameworks to create a comprehensive set of cybersecurity policies & standards. The SCRP has a 1-1 mapping relationship with the Secure Controls Framework (SCF) so it maps to over 200 leading practices!
$ 6,400.00 USD
Procedures - Security, Compliance & Resilience Program (SCRP)
This version of the SCRP is a hybrid, "best in class" approach to cybersecurity documentation that covers dozens of statutory, regulatory and contractual frameworks to create a comprehensive set of cybersecurity procedures. The SCRP has a 1-1 mapping relationship with the Secure Controls Framework (SCF) so it maps to over 200 leading practices!
Common Questions
Frequently-Asked Questions
Here are answers to common questions about HIPAA certification through the SCF: