
Quality, Expert-Derived Cybersecurity Documentation To Keep Organizations Secure, Compliant & Resilient  |  Got Questions? +1-307-241-8740
ComplianceForge

Program Governance

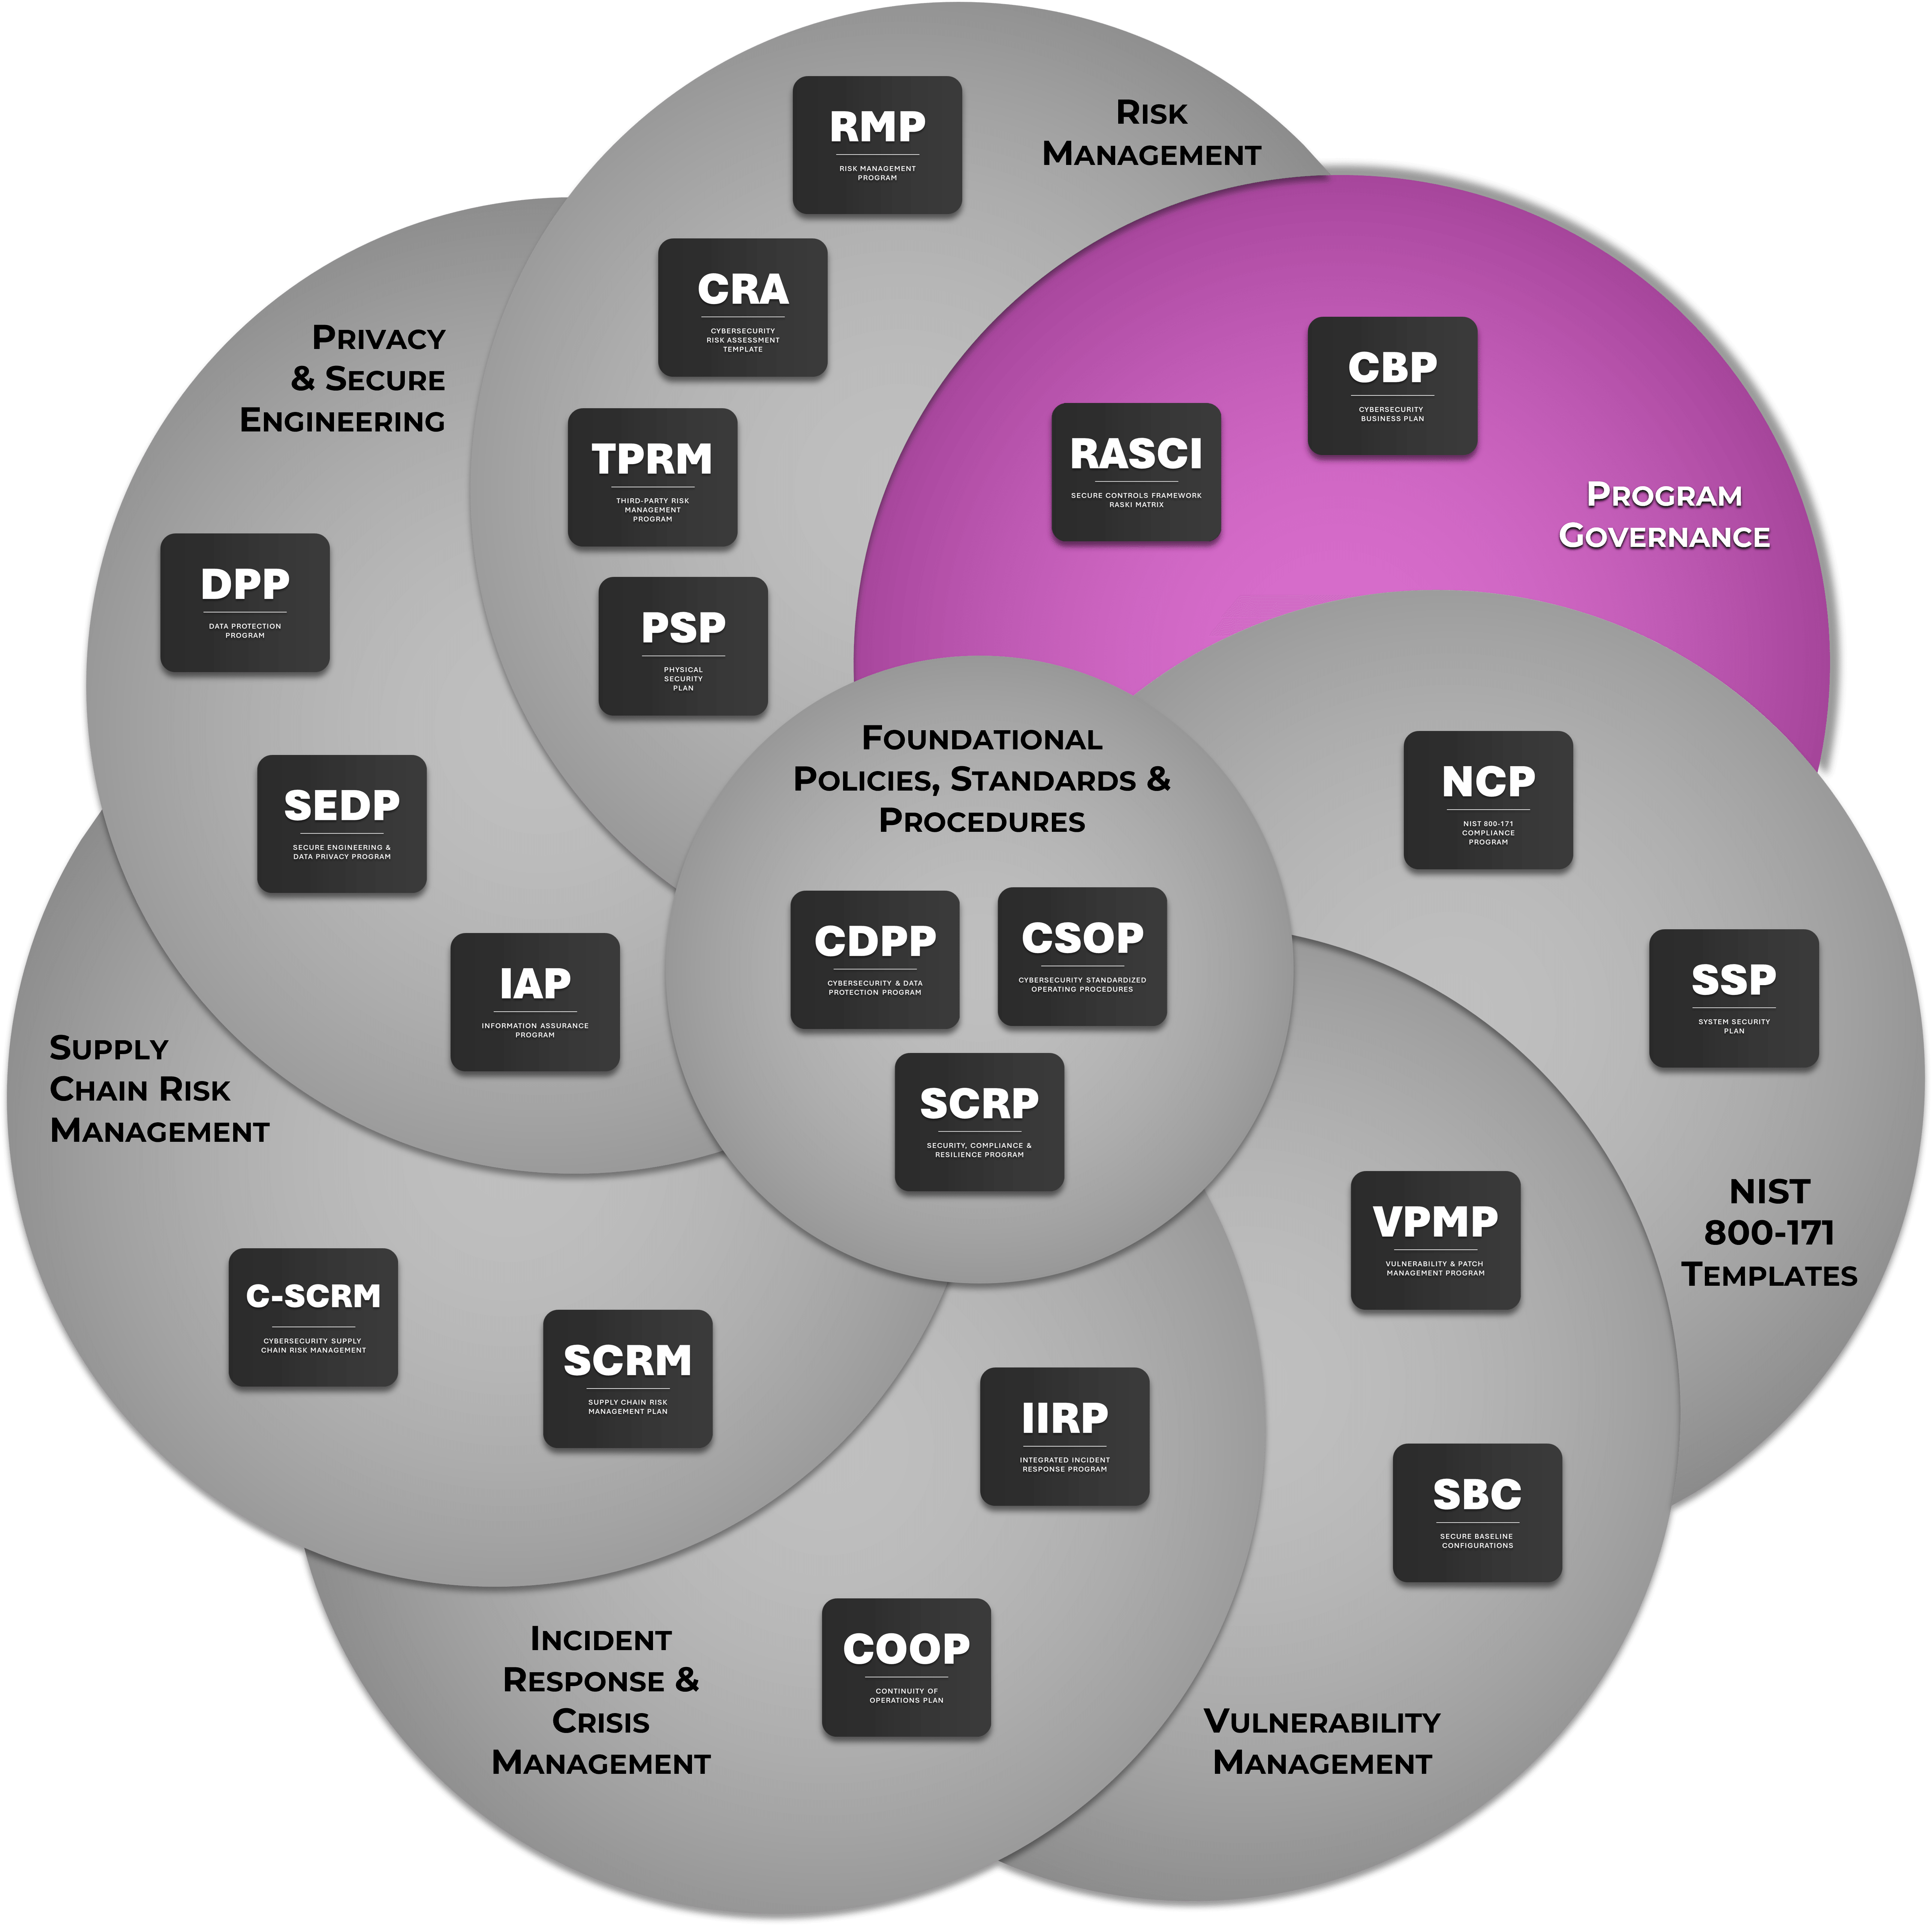
Although to have policies, standards, procedures, risk management documentation, vulnerability & patch management documentation, incident response documentation, and supply chain risk management documentation are important, it is also important to achieve program governace, which may not be wholly achievable through those common categories of documentation. The good news is that ComplianceForge has created a category for documentation that is designed to help organizations achieve governance over their cybersecurity program!.

Key Takeaways - Program Governance
  • The SCF RASCI Matrix leverages the Secure Controls Framework to address all 1,500+ of its controls and the NIST NICE Cybersecurity Workforce Framework as the foundation for the work roles and work role IDs.
  • The Cybersecurity Business Plan (CBP) is focused on the CISO level and is a department-level planning document
Category Overview

Documentation That Helps Achieve Program Governance

When you "peel back the onion", outside of policies and standards, procedures, risk management, and the other categories of documentation that ComplianceForge provides, this category of program governance was created to address products that are not directly associated with those categories but are equally as improtant. While policies and standards are designed to describe WHY something is required and WHAT needs to be done, many companies fail to create documentation to address HOW the policies and standards are actually implemented. We did the heavy lifting and created several program-level documents to address this need and the Cybersecurity Business Plan (CBP) is one of those products.

The two products in this category address two sides of cybersecurity program governance. The Cybersecurity Business Plan (CBP) is focused on the CISO level and is a department-level planning document. The SCF RASCI Matrix leverages the Secure Controls Framework (SCF) to address all 1,500+ of its controls and the NIST NICE Cybersecurity Workforce Framework as the foundation for the work roles and work role IDs.

Flower ComplianceForge Program Governance
Available Products

Available Program Governance Products

Within this category, we currently provide two (2) products that can help build governance over your organization's cybersecurity program.
$ 100.00 USD
SCF RASCI Matrix
ComplianceForge's RASCI matrix provides a practical, role-based accountability model for assigning ownership across all 1,500+ SCF cybersecurity, data privacy, compliance and resilience controls. Built on the NIST NICE Cybersecurity Workforce Framework and expanded with additional roles commonly found in Fortune 1000 organizations, this RASCI is designed to help organizations eliminate ambiguity over “who owns what” in a cybersecurity program.
Contains:
Word
Excel
PowerPoint
PDF
Examples:
Word Example
Excel Example
$ 2,175.00 USD
Cybersecurity Business Plan (CBP)
The Cybersecurity Business Plan (CBP), which some may refer to as a CISO Business Plan, is a business plan template that is specifically tailored for a cybersecurity department that is designed to support an organization's broader technology and business strategies. The CBP is entirely focused at the CISO-level, since it is a department-level planning document.
Contains:
Word
Excel
PowerPoint
PDF
Examples:
Word Example
Excel Example
Contact Us

Comprehensive Coverage

Give us a call or send us an email - we are happy to help you find the right solution for your needs!

There are a lot of choices to pick from when selecting a cybersecurity framework. If you are not sure what works best for you, you can read more here. The most common frameworks are NIST 800-53, ISO 27002, the NIST Cybersecurity Framework and the Secure Controls Framework (SCF). To do NIST CSF, ISO 27002 or NIST SP 800-53 properly, it takes more than just a set of policies and standards. While those are foundational to building a cybersecurity program aligned with that framework, there is a need for program-specific guidance that helps operationalize those policies and standards (e.g., risk management program, third-party management, vulnerability management, etc.). It is important to understand what is required to comply with NIST CSF vs ISO 27002 vs NIST SP 800-53, since there are significantly different levels of expectation.

It is important to understand that picking a cybersecurity framework is more of a business decision and less of a technical decision. Realistically, the process of selecting a cybersecurity framework must be driven by a fundamental understanding of what your organization needs to comply with from a statutory, regulatory and contractual perspective, since that understanding establishes the minimum set of requirements necessary to:

  • Not be considered negligent with reasonable expectations for cybersecurity & data protection;
  • Comply with applicable laws, regulations and contractual obligations; and
  • Implement the proper controls to secure your systems, applications and processes from reasonable threats, based on your specific business case and industry practices.

This understanding makes it easy to determine where on the "framework spectrum" (shown above) you need to focus for selecting a set of cybersecurity principles to follow. This process generally leads to selecting the NIST Cybersecurity Framework, ISO 27002, NIST SP 800-53 or SCF as a starting point.

Common Questions

Frequently-Asked Questions

Here are answers to common questions about cybersecurity program governance documentation:

What does RASCI stand for?
RASCI stands for Responsible, Accountable, Supporting, Consulted and Informed. Responsible is the person or team that carries out the work, Accountable is the single owner of the outcome, Supporting assists the responsible party, Consulted provides knowledge and input, and Informed is kept up to date on progress and quality. Only one person should be Accountable for each task or control, which is what keeps ownership clear.
What is the difference between RACI and RASCI?
RASCI adds a Supporting role to the familiar RACI model of Responsible, Accountable, Consulted and Informed. The Supporting designation identifies people or teams who help the responsible party do the work without owning it, which is common in cybersecurity, where IT operations, legal or HR often assist security staff. That extra distinction makes a control ownership matrix more realistic in organizations where execution depends on several groups.
How do you assign cybersecurity control ownership across an organization?
Assign each control to a defined work role instead of a named individual, mark one Accountable owner, and identify who executes, supports, advises and needs to be informed. Using a recognized role taxonomy keeps assignments consistent as people change jobs. The ComplianceForge SCF RASCI Matrix applies this approach to Secure Controls Framework controls, and we use the NIST NICE Workforce Framework for Cybersecurity as the foundation for its work roles, plus roles common in large enterprises.
What should a cybersecurity business plan include?
A cybersecurity business plan should explain what the security department does, where it's heading and how it supports the business. Typical sections include mission and vision, strategy with a SWOT analysis, a definition of success and value proposition, prioritized objectives, a concept of operations, mid-term and long-term plans, financial planning and target maturity levels. If you want a starting point, the ComplianceForge Cybersecurity Business Plan (CBP) is a Word template we built around these sections for CISOs and security leaders.
Why does a CISO need a cybersecurity business plan?
A CISO needs a business plan to connect security priorities and spending to the organization's broader business and technology strategy. Without one, security work tends to be reactive and hard to justify at budget time. A written plan states the department's mission, objectives and target maturity, giving executives a basis for funding decisions and for measuring progress. NIST CSF 2.0 reflects this in its GOVERN Function, covering how cybersecurity strategy is established, communicated and monitored.