The Secure Controls Framework (SCF) is a meta-framework that maps to over 200 cybersecurity and data privacy laws, regulations, and industry frameworks (e.g., NIST, ISO, GDPR, HIPAA, PCI DSS), and ComplianceForge offers structured, comprehensive, and efficient solutions based on the SCF for developing and managing cybersecurity documentation. This combination helps organizations streamline compliance efforts, manage risks effectively, and build a robust digital security program tailored to their specific needs and regulatory obligations. ComplianceForge and the SCF are highly beneficial for cybersecurity documentation for several reasons, derived from their design principles and features:
ComplianceForge is an authorized Licensed Content Provider (LCP) by the Secure Controls Framework. Authorized to sell cybersecurity and data protection documentation based on SCF controls.
ComplianceForge is an authorized SCF Licensed Content Provider (LCP). Authorized to sell SCF-based documentation.
The SCF is a metaframework mapping 200 plus laws, regulations and frameworks. ComplianceForge provides the documentation to operationalize it.
SCF-based products have 1-1 mapping between documentation and SCF controls. Policies map to domains, standards to controls.
Products save significant labor costs from researching, writing and refining cybersecurity documentation.
Available in Word and Excel formats for stand-alone use or GRC platform import.
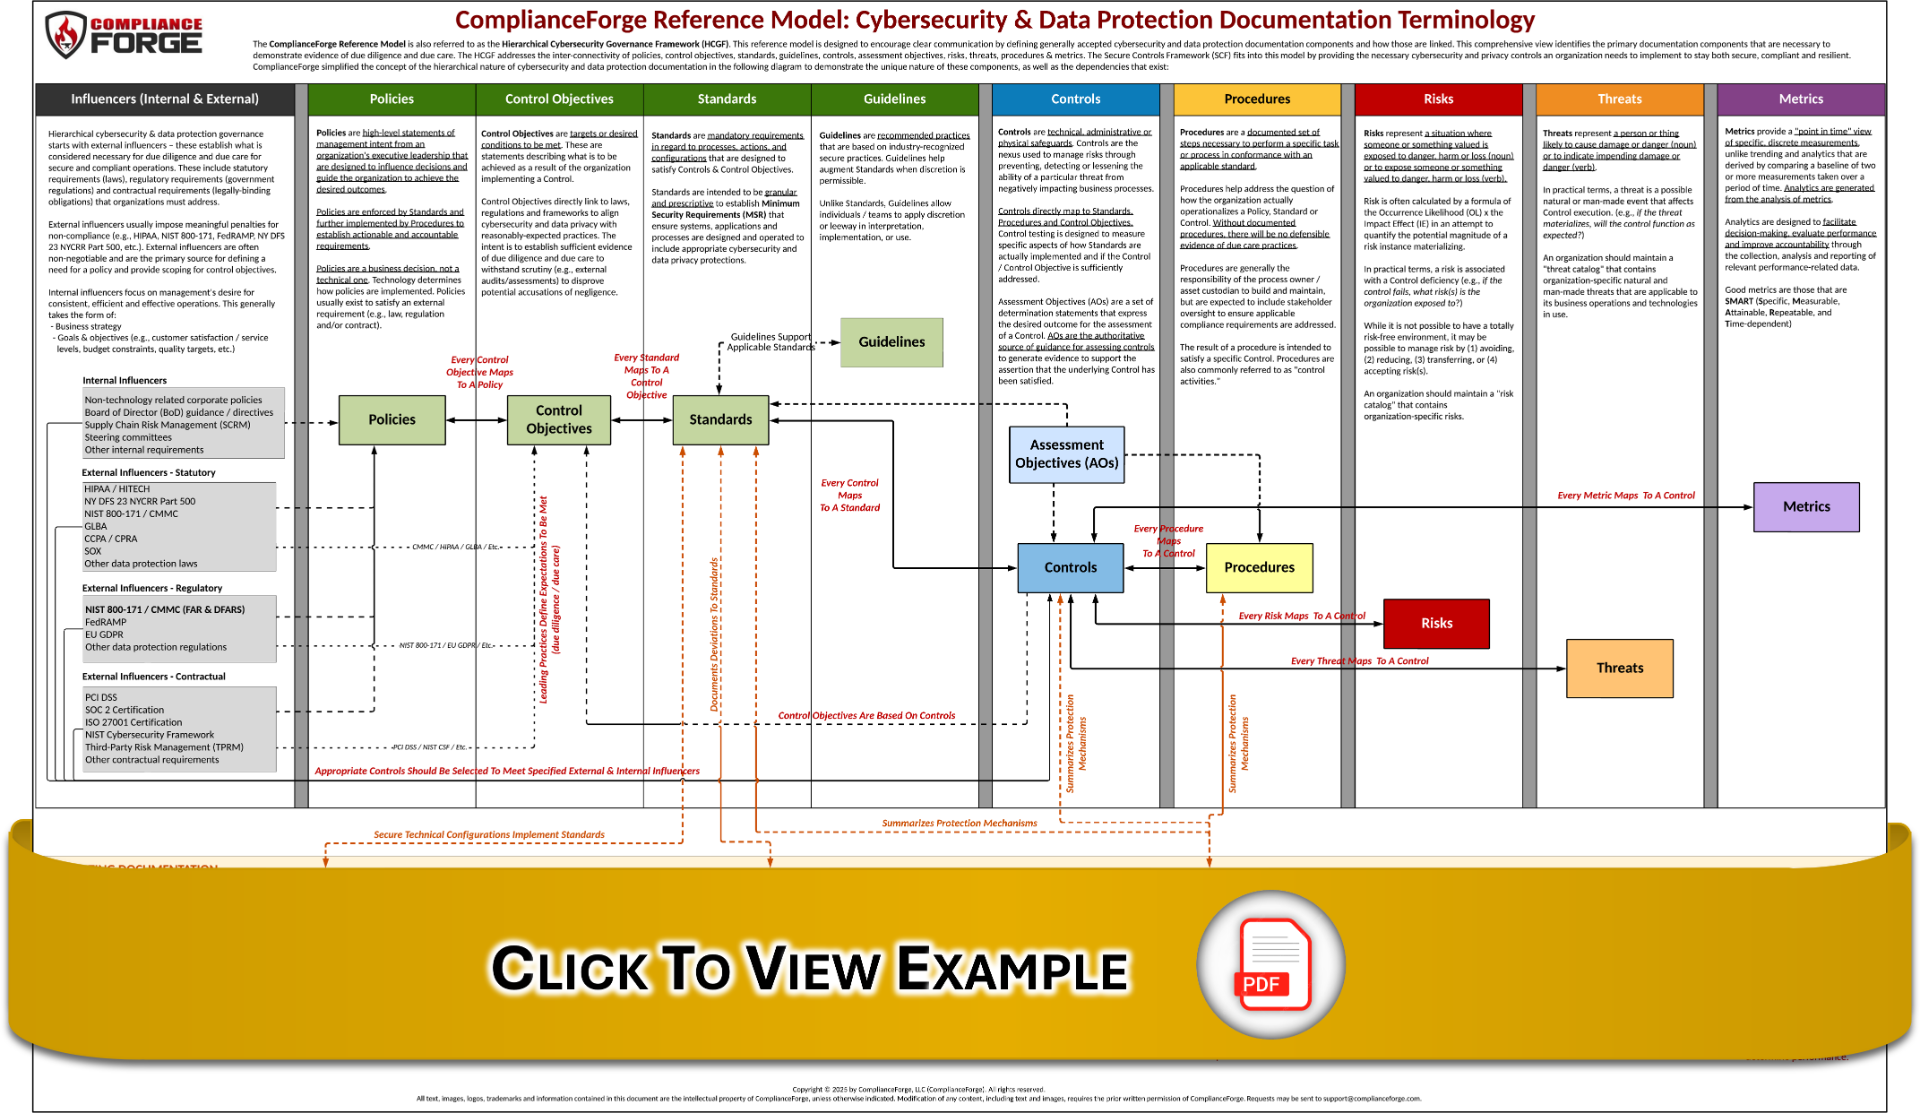
The ComplianceForge Reference Model establishes how documentation should be hierarchically structured.
Authorized Provider
What SCF LCP Means
The SCF is a metaframework that maps to over 200 cybersecurity and data privacy laws, regulations and industry frameworks (e.g. NIST, ISO, GDPR, HIPAA, PCI DSS). ComplianceForge offers structured, comprehensive and efficient solutions based on the SCF for developing and managing cybersecurity documentation. This combination helps organizations streamline compliance efforts, manage risks effectively and build a robust digital security program tailored to their specific needs and regulatory obligations.
ComplianceForge, as a Licensed Content Provider (LCP) by the Secure Controls Framework (SCF), is authorized to offer a wide range of cybersecurity and data protection documentation. This includes policies, standards, and procedures meticulously aligned with SCF controls, ensuring organizations can effectively manage compliance and security requirements. If you manage compliance in a GRC platform, see our premium GRC content.
Meta-Framework Approach
The SCF acts as a meta-framework, consolidating guidance from over 200 cybersecurity and data privacy laws, regulations, and industry frameworks (e.g., NIST, ISO, GDPR, HIPAA, PCI DSS). This significantly reduces the effort required to cross-reference multiple standards.
Hierarchical Structure
ComplianceForge documentation, based on its Hierarchical Cybersecurity Governance Framework (HCGF), provides a clear, logical structure that links policies to control objectives, standards, controls, procedures, and guidelines. This ensures consistency and traceability from high-level strategy to daily operations.
More Efficient & Saves Time
Efficiency and Time Savings
Editable Templates
ComplianceForge offers pre-written, editable templates for policies, standards, controls, and procedures. This dramatically cuts down on the time and resources organizations would otherwise spend researching, writing, and formatting their cybersecurity documentation from scratch.
Prioritized Implementation
Models like the "NIST 800-171 R3 Kill Chain" provide phased project plans, enabling organizations to prioritize efforts and avoid rework during compliance transitions.
Provides Guidance and Enhances Compliance
Enhanced Cybersecurity Compliance and Risk Management
Granular Requirements
While frameworks like NIST 800-171 Rev 3 might reduce the number of core controls, they significantly increase discrete requirements. ComplianceForge's guides help navigate these complexities, ensuring a more thorough understanding and implementation.
ComplianceForge also provides guidance on C-SCRM, a critical aspect of modern cybersecurity, helping practitioners manage cybersecurity risks across their supply chains.
Clarity and Communication
Increases Clarity and Standardizes Terminology
Standardized Terminology
ComplianceForge's documentation aims to define and link generally accepted cybersecurity and data privacy terms, promoting clear communication within the organization and with external stakeholders.
Actionable Guidance
ComplianceForge's documentation provides practical guidance, helping organizations to become not only just "compliant" but also truly "secure" by detailing how to operationalize cybersecurity and data privacy.
ComplianceForge's Solutions
What SCF-Based Documentation Does ComplianceForge Sell?
ComplianceForge offers the following SCF-based documentation templates:
$ 10,400.00 USD
Policies & Standards - Security, Compliance & Resilience Program (SCRP)
This version of the SCRP is a hybrid, "best in class" approach to cybersecurity documentation that covers dozens of statutory, regulatory and contractual frameworks to create a comprehensive set of cybersecurity policies & standards. The SCRP has a 1-1 mapping relationship with the Secure Controls Framework (SCF) so it maps to over 200 leading practices!
This version of the Cybersecurity & Data Protection Program (CDPP) is based on the NIST Cybersecurity Framework 2.0 (NIST CSF 2.0) framework. It contains the necessary NIST CSF policies and standards that help achieve compliance with NIST CSF. You get fully-editable Microsoft Word and Excel documents that you can customize for your specific needs.
This version of the Cybersecurity & Data Protection Program (CDPP) is based on the ISO 27001 / 27002 framework. It contains the necessary ISO 27001 / 27002 policies and standards that help achieve compliance. You get fully-editable Microsoft Word and Excel documents that you can customize for your specific needs.
Procedures - Security, Compliance & Resilience Program (SCRP)
This version of the SCRP is a hybrid, "best in class" approach to cybersecurity documentation that covers dozens of statutory, regulatory and contractual frameworks to create a comprehensive set of cybersecurity procedures. The SCRP has a 1-1 mapping relationship with the Secure Controls Framework (SCF) so it maps to over 200 leading practices!
This version of the Cybersecurity Standardized Operating Procedures (CSOP) is based on the NIST Cybersecurity Framework 2.0 (NIST CSF 2.0) framework. It contains the necessary NIST CSF procedures that help achieve compliance with NIST CSF. You get fully-editable Microsoft Word documents that you can customize for your specific needs.
This version of the Cybersecurity Standardized Operating Procedures (CSOP) is based on the ISO 27001 / 27002 framework. It contains the necessary ISO 27001 / 27002 procedures that help achieve compliance with ISO 27001 / 27002. You get fully-editable Microsoft Word documents that you can customize for your specific needs.
The NCP is designed to fit the needs of small to medium businesses in need of a “square peg for a square hole” to singularly address NIST 800-171 and CMMC compliance requirements. The NCP is "battle tested" - our clients have successfully passed DIBCAC assessments with this documentation, including a CMMC Third-Party Assessment Organization (C3PAO).
ComplianceForge also offers multiple discounted bundles, so please take a look and see if any of our bundles can help your organization! If there are specific products you want, you can create your own custom bundle by adding the products to your cart, submitting a quote, and we will work with you to get the best discount!
Examples
Example SCF Policies, Standards & Procedures
The ComplianceForge Reference Model establishes how cybersecurity and data privacy documentation is meant to be built. This documentation model that leverages industry-recognized terminology to logically arrange these documentation components into their rightful order. This model creates an approach to architecting documentation that is concise, scalable and comprehensive. When that is all laid out properly, an organization's cybersecurity and data protection documentation should be hierarchical and linked from policies all the way through metrics. The swimlane diagram shown below (click for a larger PDF) defines the terminology and demonstrates the linkages between these various documentation components.
Cybersecurity & data protection documentation needs to usable. This means the documentation needs to be written clearly, concisely and in a business-context language that users can understand. By doing so, users will be able to find the information they are looking for and that will lead to IT security best practices being implemented throughout your company. Additionally, having good cybersecurity documentation can be “half the battle” when preparing for an audit, since it shows that effort went into the program and key requirements can be easily found.
The PDF document shown below provides two, side-by-side examples from policies all the way through metrics, so you can see what the actual content looks like.
Common Questions
Frequently-Asked Questions
Here are answers to common questions about SCF Licensed Content Providers:
What is an SCF Licensed Content Provider (LCP)?
An SCF Licensed Content Provider (LCP) is an organization authorized by the SCF Council to sell derivative works of the Secure Controls Framework, such as SCF-based policies, standards and procedures. The license matters because the free SCF is published under a Creative Commons license that does not allow modified versions to be distributed. LCPs are one of the recognized roles in the SCR CAP ecosystem, alongside 3PAOs, Registered Provider Organizations and Control Assurance Tools.
Is ComplianceForge an authorized SCF Licensed Content Provider?
Yes, ComplianceForge is an authorized SCF Licensed Content Provider, which allows us to sell cybersecurity and data protection documentation built on SCF controls, and you'll find us on the Secure Controls Framework's list of LCPs. Our SCF-based products use a 1-1 mapping, where policies align to SCF domains and standards align to individual SCF controls, so you can trace the documentation directly back to the framework.
Can I share or sell documents based on the SCF without a license?
No, distributing or selling modified SCF content requires a commercial license. The SCF is free under the Creative Commons Attribution-NoDerivatives 4.0 International license, which lets an organization modify the content for its own internal use but prohibits sharing derivative works. The SCF states that this restriction also covers AI-generated derivative content. Using SCF content inside a GRC platform without creating derivative works does not require a commercial license.
Why buy SCF-based policies if the Secure Controls Framework is free?
The free SCF provides controls, mappings, risk and threat catalogs, maturity criteria and assessment objectives, but it does not include the written policies, standards and procedures an organization needs to run and prove its program. Writing that documentation and mapping it to each control takes significant time. Licensed SCF-based documentation is prewritten and editable, so internal staff spend their time tailoring content instead of researching and drafting it from scratch.
How can I verify an authorized SCF Licensed Content Provider?
You can verify an LCP by checking the SCF Licensed Content Providers listing in the marketplace on the Secure Controls Framework website. The SCF Council issues the LCP designation to Tier 2 SCF Commercial Licensees, because that license tier authorizes broad SCF-based documentation such as policies, standards and procedures. A Tier 1 license, which is designed for GRC platforms, does not carry the LCP designation. You'll find ComplianceForge on the SCF's list of Licensed Content Providers.