Key Takeaways - CIS Critical Security Controls (CSC)
- CIS Critical Security Controls (CSC), formerly SANS Top 20, are a prioritized, actionable set of cybersecurity practices maintained by the Center for Internet Security.
- Organized into three Implementation Groups (IGs). IG1 (essential cyber hygiene), IG2 (plus operational complexity), IG3 (sophisticated adversaries).
- 18 controls with 153 safeguards across the current version, focused on the highest-impact defensive actions first.
- Particularly popular with mid-market organizations looking for practical, actionable controls without the complexity of NIST 800-53.
- ComplianceForge documentation maps CIS CSC to NIST CSF, NIST 800-53, ISO 27001 and 200 plus frameworks through the SCF.
Safety ComponentTaking ICS, OT and IOT Into Account
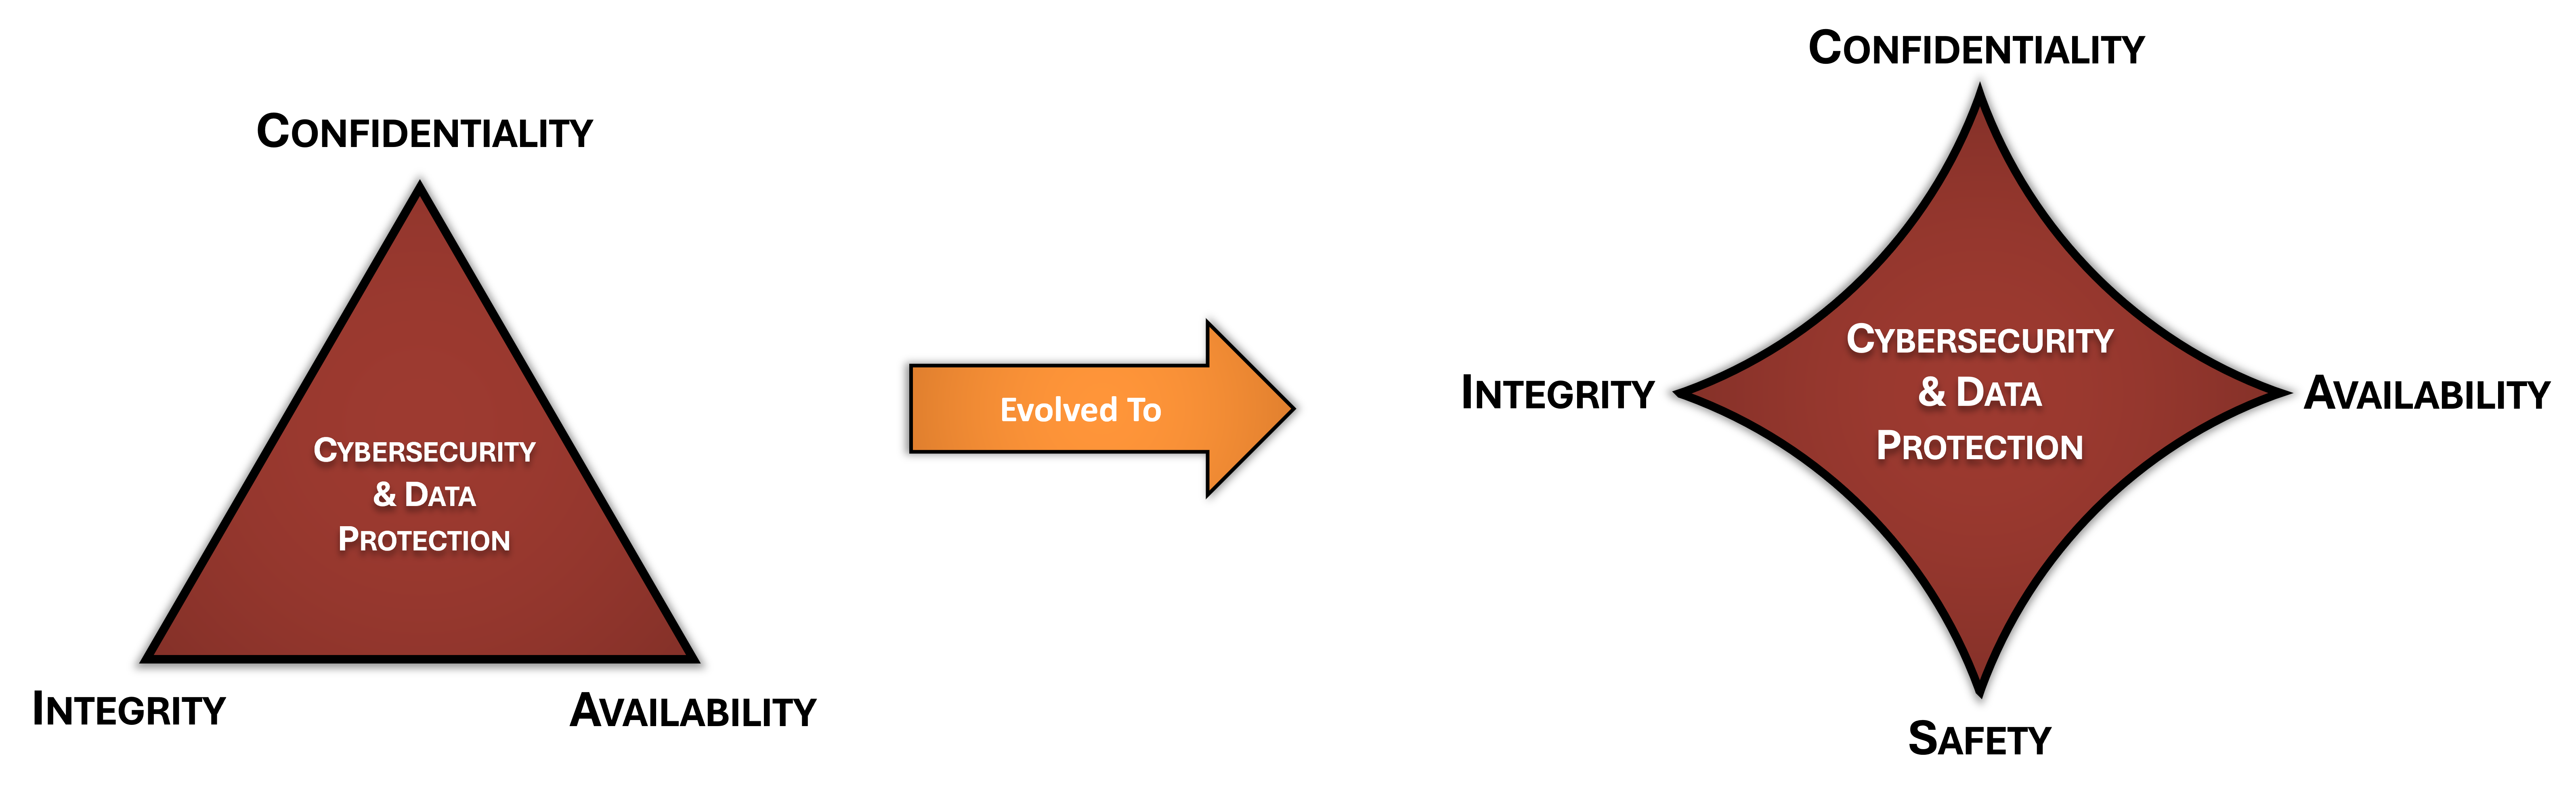
For years, the “CIA Triad” stood as the foundation for what a security program was designed to address – the Confidentiality, Integrity and Availability of both systems and data. That has now changed, since there are real-world safety considerations from Operational Technology (OT) and the Internet of Things (IoT). This has caused the evolution of the CIA Triad into the Confidentiality, Integrity, Availability and Safety (CIAS) model.
The SCRP is designed around the CIAS model by adopting the best of leading security frameworks.
Import-Ready For GRC ToolsThe SCRP Comes In Both Microsoft Word & Excel Formats
The DSP is ready to import into your Governance, Risk & Compliance (GRC) solution, since it comes in both Microsoft Word and Excel formats. This makes the import from Excel easy. For many GRC tools, this provides you the ability to perform your customization and collaboration directly from your GRC portal.
If you do not currently have a GRC tool, but want to deploy the DSP from a user-friendly internal website, we can help with that. We offer a fixed-cost service to convert the DSP into an internal website using GRAV, a Content Management System (CMS). If that interests you, please contact us at support@compianceforge.com and we can provide you with more details on that option.
The Excel version of the DSP comes with the following content so it is easy to import into a GRC solution (e.g., ZenGRC, MetricStream, Ostendio, Archer, RSAM, MetricStream, etc.):
Policy statements
Control objectives
Standards
Guidance
Controls
Metrics (KPIs & KRIs)
Indicators of Compromise (IoC)
Indicators of Exposure (IoC)
Target Audience Applicability
Scoping - Basic or Enhanced Requirement
Recommended roles / teams with responsibility for each standard
Common QuestionsFrequently-Asked Questions
Here are answers to common questions about the CIS Critical Security Controls:
How many CIS Controls are there?
There are 18 CIS Controls, which contain 153 Safeguards, in CIS Controls v8 and v8.1. The Center for Internet Security reduced the number of top-level Controls from 20 to 18 when it released version 8 in May 2021. Documentation that still refers to the CIS Top 20 is based on an earlier version and should be updated so that control references and mappings match the current Controls and Safeguards.
What is the current version of the CIS Controls?
The current version is CIS Critical Security Controls v8.1, an iterative update to version 8 published by the Center for Internet Security (CIS). Version 8.1 realigned its mappings to NIST CSF 2.0, revised asset classes, expanded glossary definitions, fixed minor errors and clarified some Safeguard descriptions. CIS says the update was designed to maintain continuity for existing users, with little to no change for organizations already working from version 8.
What are the CIS Controls Implementation Groups?
CIS Controls Implementation Groups (IGs) are three tiers that prioritize Safeguards according to an enterprise's resources and risk. IG1 is essential cyber hygiene, a set of 56 Safeguards that CIS describes as an emerging minimum standard of information security for all enterprises. IG2 builds on IG1 with additional Safeguards for organizations with greater resources and risk, and IG3 includes all of the Controls and Safeguards. An organization can treat IG1 as its first milestone.
Do the CIS Controls map to NIST CSF 2.0?
Yes, CIS Controls v8.1 realigned its NIST CSF security function mappings to match NIST CSF 2.0, so its Safeguards can be read against CSF 2.0 Functions. That makes the CIS Controls a practical way to put CSF outcomes into action, since the CSF itself does not prescribe how outcomes are achieved. A metaframework such as the Secure Controls Framework (SCF) also maps both the CIS Controls and NIST CSF, along with more than 200 other laws, regulations and frameworks.
Which ComplianceForge product covers the CIS Controls?
ComplianceForge addresses the CIS Controls with the Security, Compliance & Resilience Program (SCRP), which we designed for organizations that must align with several frameworks at once. You'll get the SCRP in Microsoft Word and Excel, and the Excel version is built for import into a GRC platform. It includes policy statements, control objectives, standards, controls, metrics and recommended roles, and it covers more than 200 laws, regulations and frameworks beyond CIS.
