Key Takeaways - NIST SP 800-53 R5 (Moderate)
- NIST SP 800-53 Rev 5 is the most comprehensive US Government cybersecurity control catalog. The de facto standard for federal systems.
- The moderate baseline covers Low and Moderate impact systems. This is the baseline from which NIST 800-171 was derived and what FIPS 199 / 200 requires for CUI.
- 20 control families covering everything from access control through supply chain risk management. Significantly more comprehensive than NIST 800-171 alone.
- ComplianceForge offers four tiers from foundational policies to near-turnkey documentation solutions.
- Also available in High baseline for organizations handling the most sensitive systems and data.
OverviewNIST 800-53 Rev 5 Moderate Baseline Solutions
When you look at it from a sliding scale of good, better, great or awesome, we have a few options for you to meet your needs and budget to align your company with NIST 800-53. The product names you see in the various packages below map into the matrix shown above to show you how that maps into NIST 800-53. If you also need documented procedures for the moderate baseline, see our NIST 800-53 procedures template.
This version of the Cybersecurity & Data Protection Program (CDPP) is based on the NIST 800-53 rev5 framework. It contains cybersecurity policies and standards that align with NIST 800-53 (including NIST 800-171 & CMMC requirements). You get fully-editable Microsoft Word and Excel documents that you can customize for your specific needs.
PSP Bundle 3 is the foundational NIST 800-53 R5 Moderate documentation set from ComplianceForge, built for FedRAMP Moderate, FISMA Moderate and federal civilian agency contractor work, or for organizations that want stronger control coverage than NIST CSF or ISO 27001. It pairs our editable NIST 800-53 R5 policies and standards (CDPP) with the matching procedures (CSOP), so what your organization requires and how your team carries it out are written to the same framework.
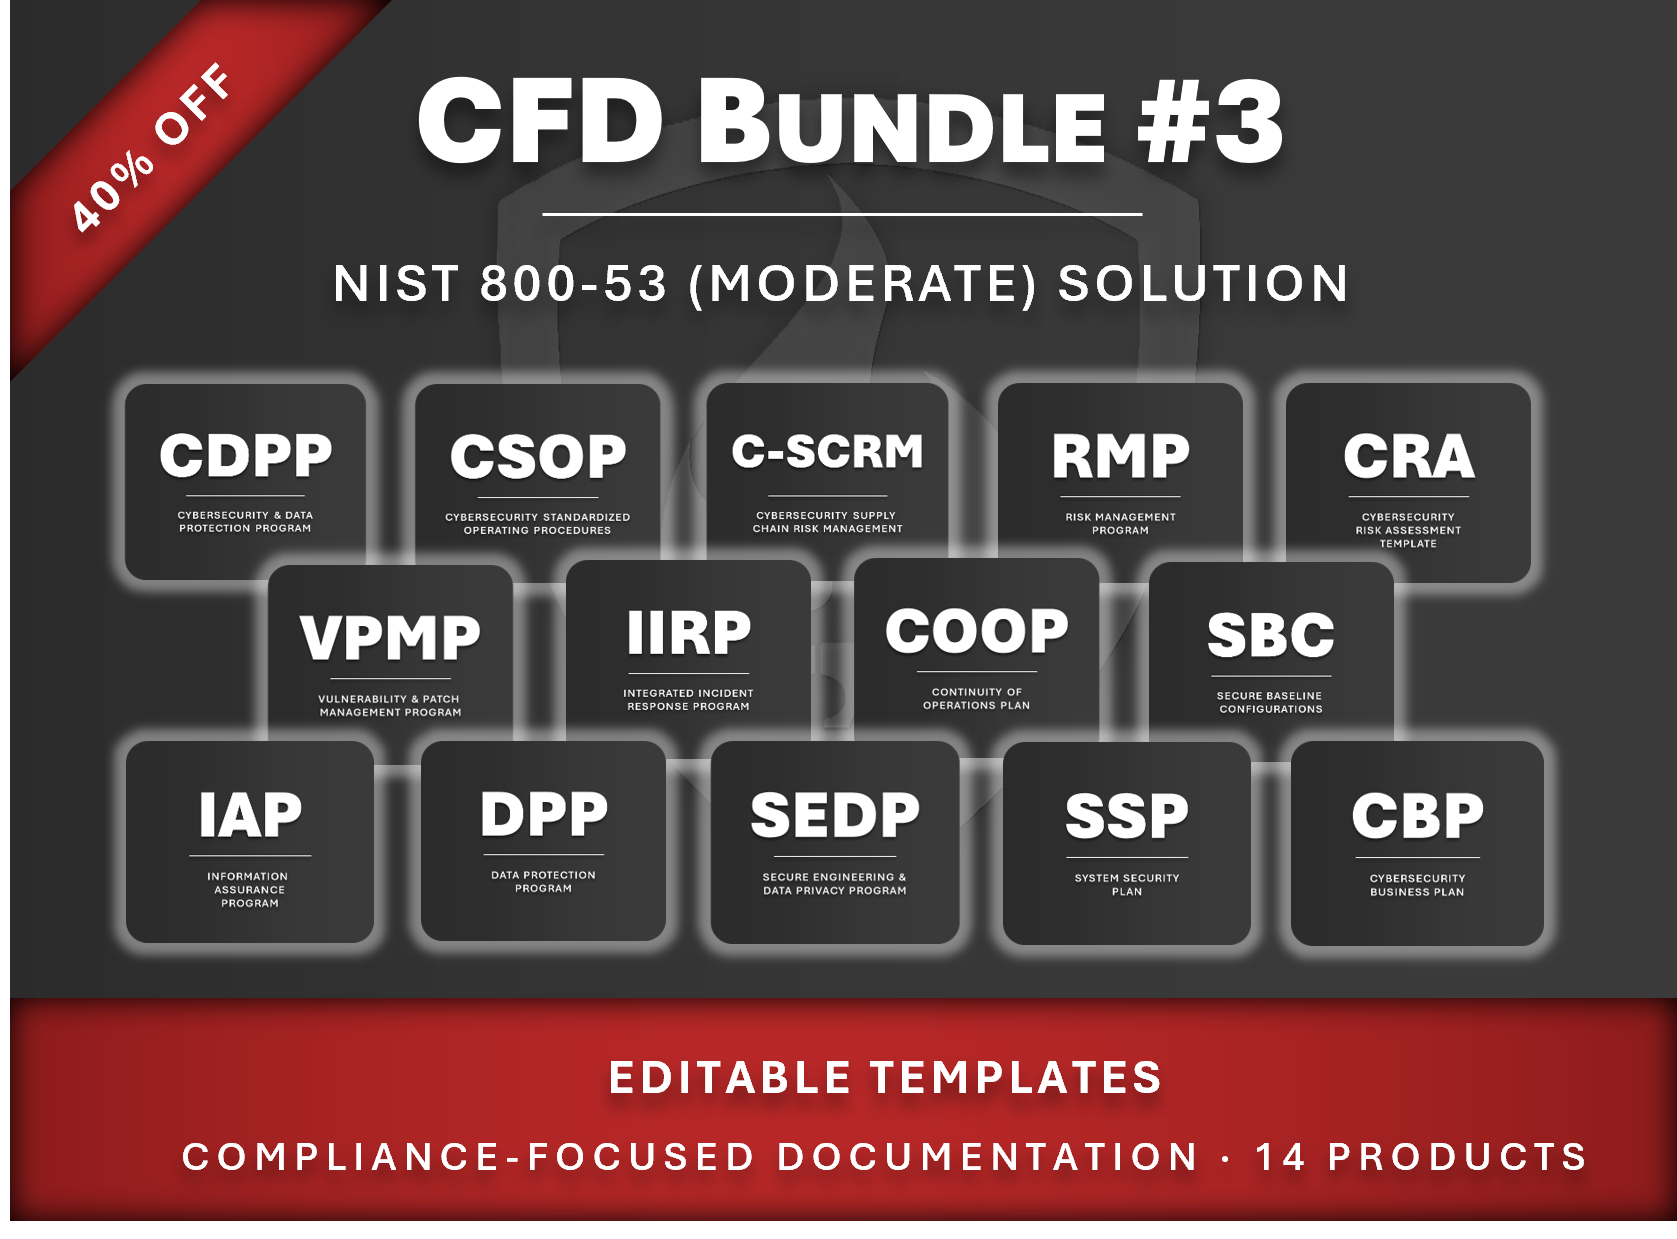
CFD Bundle 3 is the full-program NIST 800-53 R5 Moderate documentation set from ComplianceForge, with fourteen (14) coordinated products. Beyond the policies, standards and procedures, it covers risk management, risk assessments, vulnerability management, incident response, continuity of operations, secure configurations, information assurance, secure engineering, supply chain risk, data privacy, a NIST 800-171 SSP template and a cybersecurity business plan, all built on the same framework.
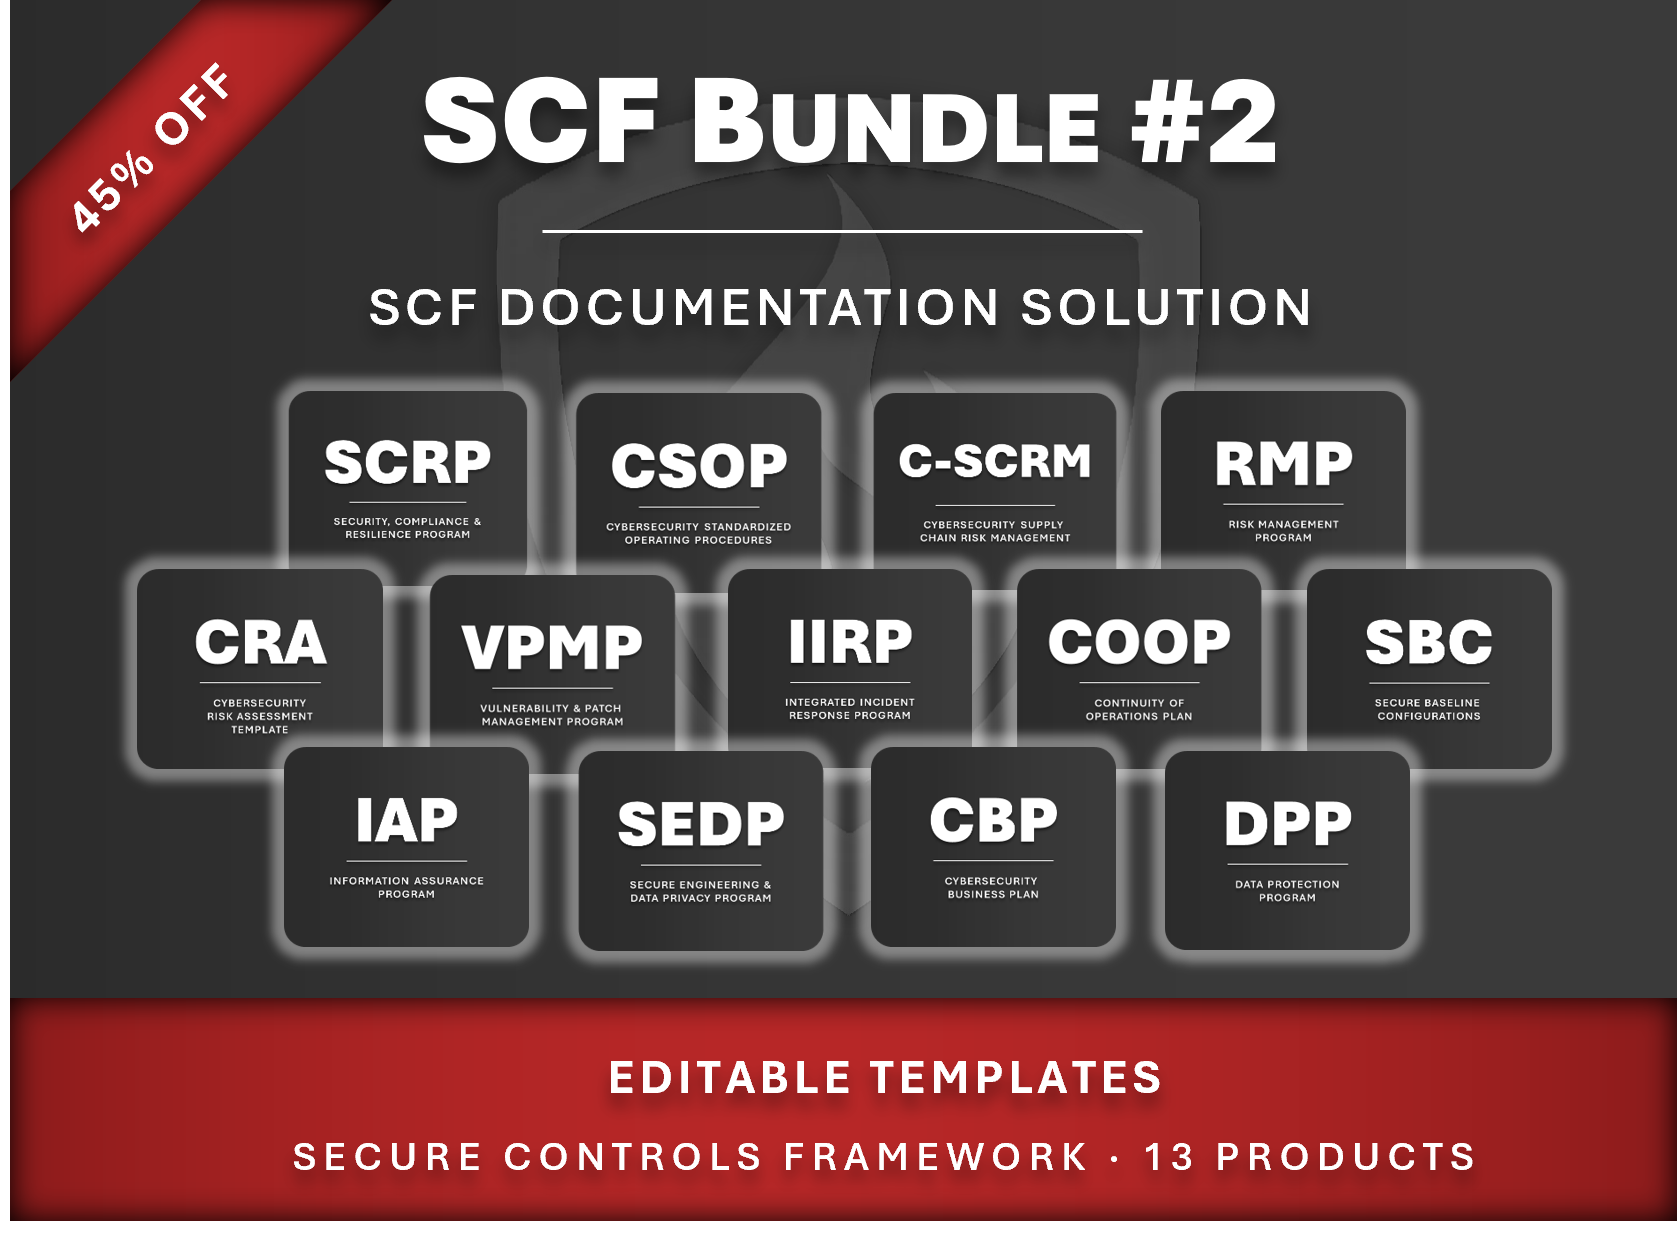
SCF Bundle 2 is the most comprehensive Secure Controls Framework (SCF) documentation set from ComplianceForge, with thirteen (13) coordinated products built on the Security, Compliance & Resilience Program (SCRP), which maps to 200+ laws, regulations & frameworks. Beyond the policies, standards and procedures, it covers risk management, risk assessments, vulnerability management, incident response, continuity of operations, secure configurations, information assurance, secure engineering, supply chain risk, data privacy and a cybersecurity business plan.
What problems Are There?What Problem Does ComplianceForge Solve?
Lack of In House Security Experience
Writing security documentation is a skill that many good cybersecurity professionals simple are not proficient at and avoid the task at all cost. Tasking your security analysts and engineers to write comprehensive documentation means you are actively taking them away from protecting and defending your network, which is not a wise use of their time. ComplianceForge offers cybersecurity documentation solutions that can save your organization significant time and money!
Audit Failures
Security documentation does not age gracefully like a fine wine. Outdated documentation leads to gaps that expose organizations to audit failures and system compromises. Our documentation provides mapping to leading security frameworks to show you exactly what is required to both stay secure and compliant. Being editable documentation, you are able to easily maintain it as your needs or technologies change.
Vendor Requirements
It is very common for clients and partners to request evidence of a security program and this includes policies and standards. Our documentation solutions provide this evidence!
How Does ComplianceForge Help?Clear Solution To Problems
Clear Documentation
ComplianceForge provides comprehensive documentation that can prove your security program exists. This equates to a time saving of hundreds of hours and tens of thousands of dollars in staff and consultant expenses!
Time Savings
Our cybersecurity documentation can provide your organization with a semi-customized solution that requires minimal resources to fine tune for your organization's specific needs.
Alignment With Leading Practices
Our documentation is mapped to NIST 800-53, as well as other leading security frameworks!
Common QuestionsFrequently Asked Questions (FAQs)
Here are answers to common questions about NIST SP 800-53 Rev 5:
What is the NIST 800-53 moderate baseline?
The NIST 800-53 moderate baseline is the set of controls that NIST SP 800-53B assigns to moderate-impact systems. A system is moderate impact when at least one of its security objectives (confidentiality, integrity or availability) is rated moderate and none is rated high. Under FIPS 199, a moderate impact means a loss could have a serious adverse effect on organizational operations, assets or individuals. Federal agencies must apply a baseline, and other organizations may use it voluntarily.
Is NIST SP 800-53 Rev 4 still valid?
No, NIST withdrew SP 800-53 Rev 4 on September 23, 2021, one year after Rev 5 was published, so Rev 5 is the version to use. Rev 5 has since received minor releases, most recently Release 5.2.0 on August 27, 2025. The NIST SP 800-53 Rev 5 page also links a Rev 4 to Rev 5 comparison workbook, which helps organizations update older control mappings and documentation.
How is NIST 800-171 related to the NIST 800-53 moderate baseline?
NIST SP 800-171 Rev 3 is derived from the NIST SP 800-53 moderate baseline. NIST started with the moderate baseline controls in SP 800-53B and tailored out controls that are primarily federal responsibilities, are not directly related to protecting the confidentiality of CUI, or are adequately addressed by other controls. As a result, an organization that implements the moderate baseline covers much of NIST SP 800-171, plus controls that SP 800-171 omits.
Do private companies have to comply with NIST 800-53?
Generally not, unless a contract or customer requires it. NIST states that implementing a minimum set of SP 800-53 controls is mandatory to protect federal information and information systems, while nongovernmental organizations may use SP 800-53B on a voluntary basis. Some private companies still adopt the moderate baseline because it is a detailed, widely recognized control catalog with published mappings to other frameworks such as the NIST Cybersecurity Framework and ISO/IEC 27001.
What NIST 800-53 moderate baseline documentation does ComplianceForge offer?
ComplianceForge offers editable policies and standards for the NIST 800-53 R5 moderate baseline, and that documentation also addresses NIST SP 800-171 and CMMC requirements. PSP Bundle 3: NIST 800-53 R5 (Moderate) adds procedures written for low and moderate impact systems, and CFD Bundle 3: NIST 800-53 R5 (Moderate) expands that to fourteen products. We offer our products in Word, Excel, PowerPoint and PDF formats, so you can customize them to fit your organization.