Quality, Expert-Derived Cybersecurity Documentation To Keep Organizations Secure, Compliant & Resilient  |  Got Questions? +1-307-241-8740
ComplianceForge

ComplianceForge Blogs

Cybersecurity compliance is a moving target that more and more complex with time. Here, we cut through the noise and provide clear, straightforward guidance on the frameworks that actually matter to your business, among other topics. Outside of selling cybersecurity documentation, our goal is to help you move past the paperwork and focus on building a truly resilient organization by helping build your knowledge on key concepts.
ISO 27001 and SOC 2 Policy Templates: Buy One Multi-Framework Set or Two?
ComplianceForge
·
October 14, 2026
Incident Response Plan Template: What to Document Before CIRCIA Reporting Starts
ComplianceForge
·
October 12, 2026
NIS2 Policies and Procedures: How to Build One Document Set for NIS2 and ISO 27001
ComplianceForge
·
October 7, 2026
How to Choose Policies and Standards to Load Into Your GRC Platform
ComplianceForge
·
October 5, 2026
Cybersecurity Metrics: What to Report to Leadership
ComplianceForge
·
October 5, 2026
What Policies Does SOC 2 Require? A Documentation Checklist
ComplianceForge
·
October 2, 2026
How to Write Cybersecurity Procedures That Assessors Accept
ComplianceForge
·
October 1, 2026
NIST 800-171 Rev 3 Assessment Objectives: What Assessors Check
ComplianceForge
·
September 30, 2026
How to Implement NIST CSF 2.0 Controls With Documentation That Scales
ComplianceForge
·
September 29, 2026
Compliance Audit Readiness Checklist: What Your Documentation Must Prove
ComplianceForge
·
September 28, 2026
What is the difference between a policy, standard and procedure for NIST SP 800-171?
ComplianceForge
·
August 24, 2026
What Documentation You Need for a CMMC Self-Assessment: SSP, POA&M, Policies and Procedures
ComplianceForge Support
·
July 27, 2026
The CMMC Compliance Checklist for an Internal Self-Assessment
ComplianceForge Support
·
July 24, 2026
CMMC Self-Assessment vs C3PAO Assessment: What Changed and What You Still Have To Prove
ComplianceForge Support
·
July 22, 2026
How To Prepare for a NIST 800-171 Self-Assessment: An Internal Assessment Playbook
ComplianceForge Support
·
July 20, 2026
NIST 800-171 Rev 2 vs Rev 3 During the CMMC Pause: Which Version Should Your Self-Assessment Follow?
ComplianceForge Support
·
July 17, 2026
Department of War Suspends CMMC Phase II: What the Self-Assessment Pivot Means for Your Contracts
ComplianceForge Support
·
July 15, 2026
What Options Exist for NIST 800-171 Rev 3 Documentation Templates
ComplianceForge Support
·
July 10, 2026
Cybersecurity Awareness Month Special
ComplianceForge Support
·
October 24, 2025
CMMC On-Site Assessments Are Optional
ComplianceForge
·
September 9, 2025
DoD ICT-SCRM Requirements
ComplianceForge
·
September 3, 2025
DoD COTS Risk Categories
ComplianceForge
·
September 2, 2025
Golden Dome for America (GDA) Cybersecurity Requirements
ComplianceForge Support
·
August 25, 2025
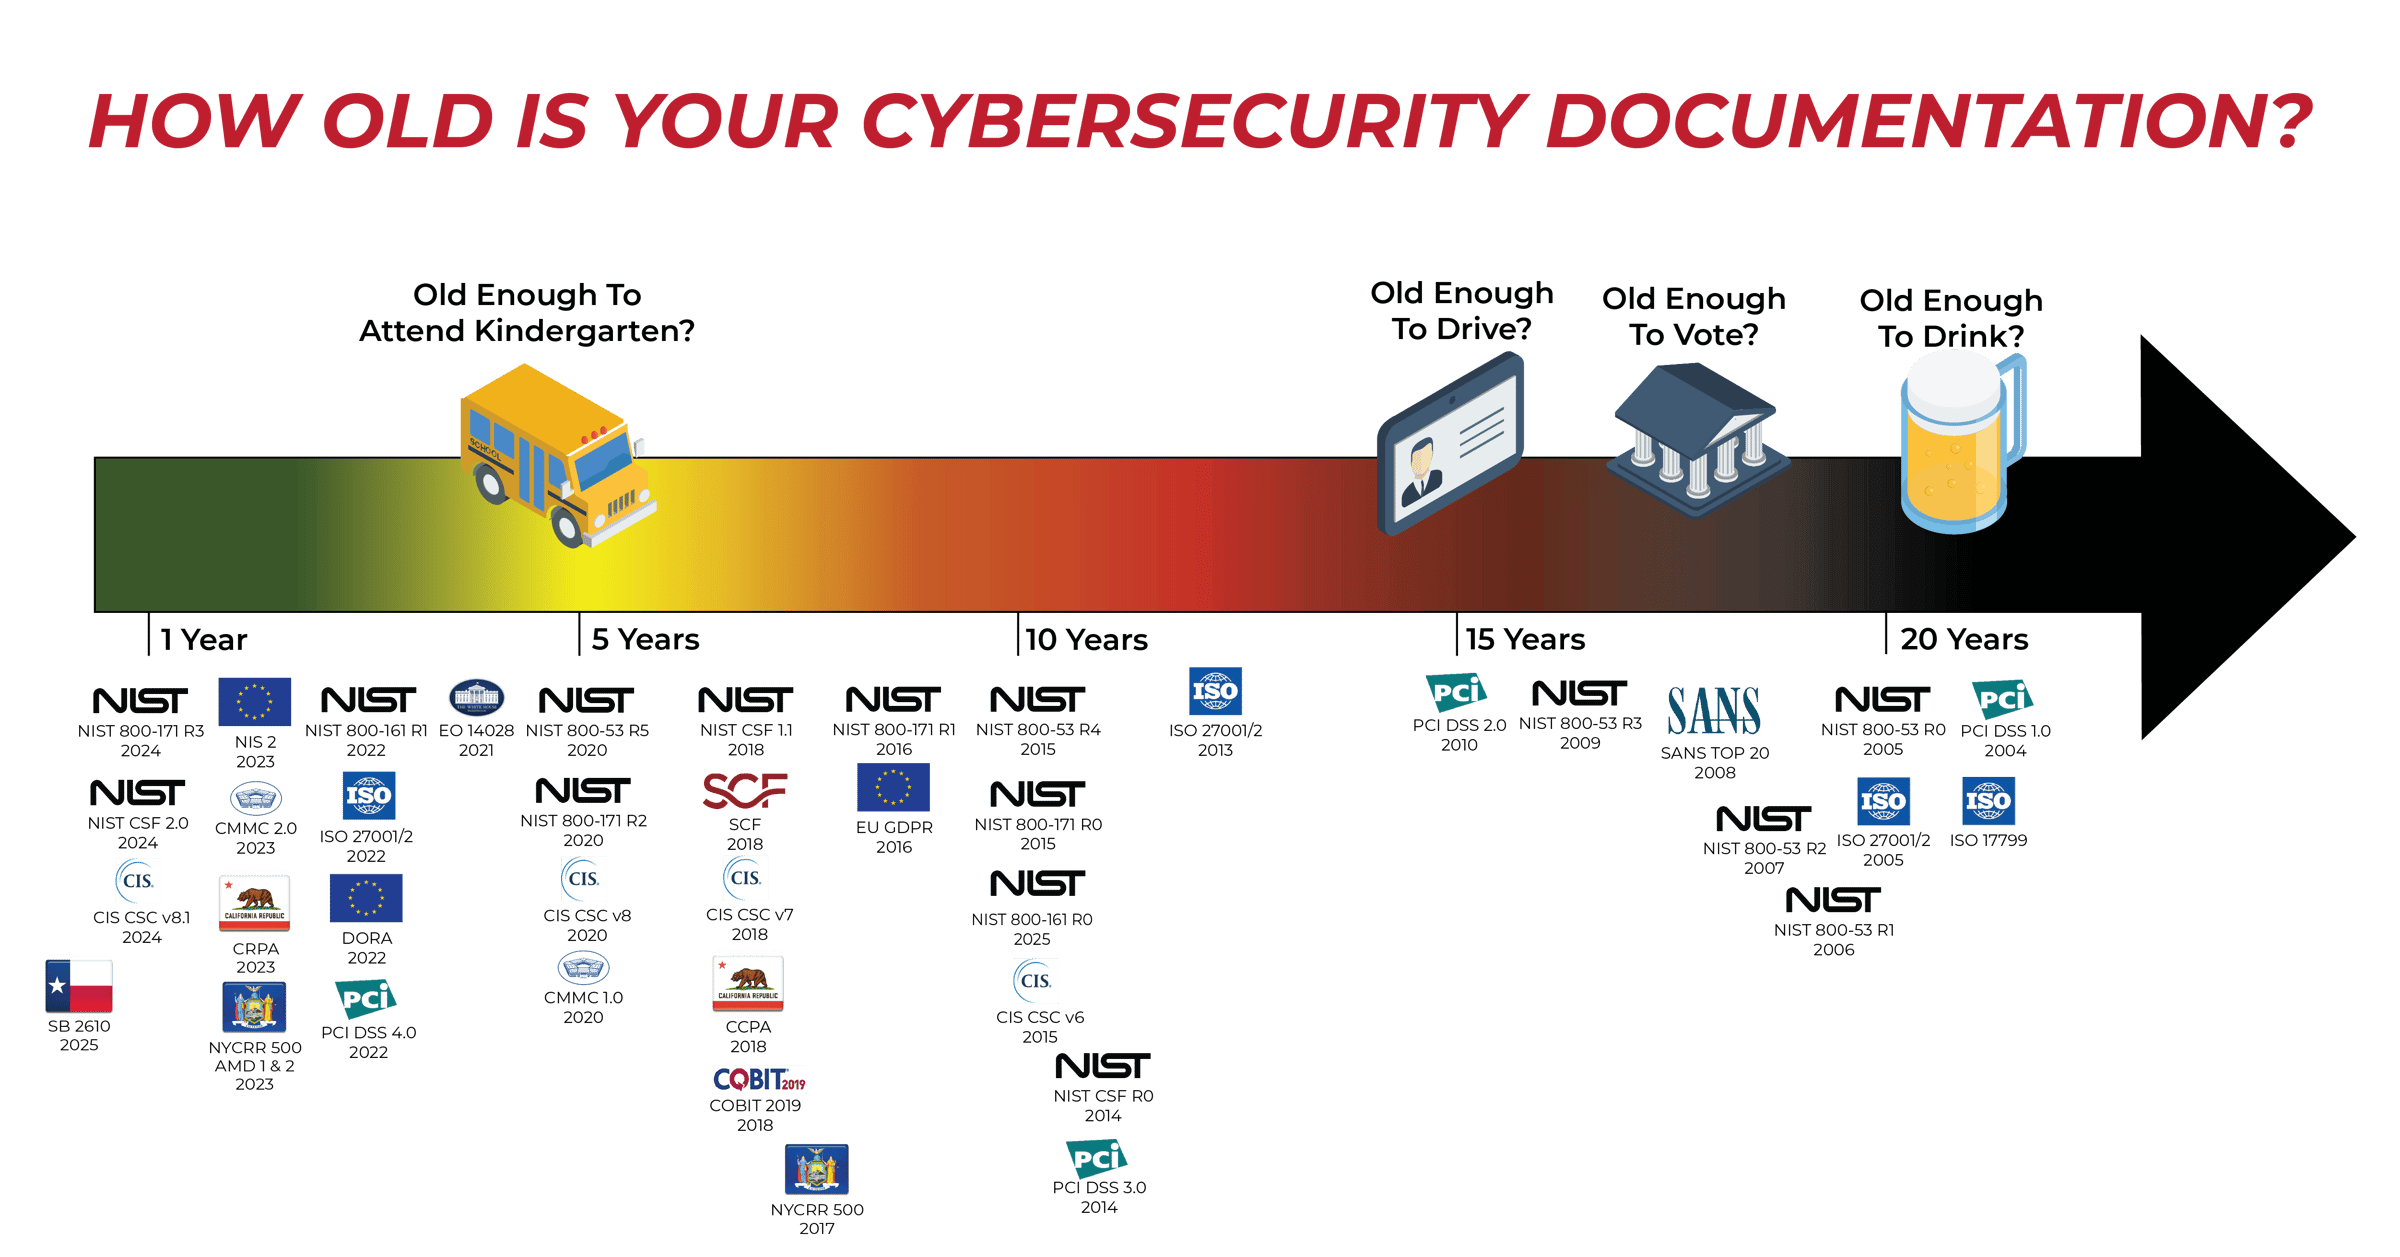
How Old Is Your Cybersecurity Documentation?
ComplianceForge
·
July 18, 2025
NIST 800-171 OPDs In Excel?
ComplianceForge Support
·
July 18, 2025