
Quality, Expert-Derived Cybersecurity Documentation To Keep Organizations Secure, Compliant & Resilient  |  Got Questions? +1-307-241-8740
ComplianceForge

Cybersecurity Standardized Operating Procedures (CSOP), SCF Version

ComplianceForge is a Licensed Content Provider (LCP) by the Secure Controls Framework (SCF). The SCRP's CSOP provides the necessary policies, control objectives, standards, guidelines and metrics to operationalize the SCF for your organization.

Key Takeaways - SCF Cybersecurity Standardized Operating Procedures (CSOP)
  • The SCF CSOP contains over 1,500 editable procedure statements with 1-1 mapping to SCF controls.
  • Approximately a 90% solution. ComplianceForge did the heavy lifting; you fine-tune with your organization's specifics.
  • Available in Word and Excel formats for stand-alone use, wiki integration or GRC platform import.
  • Saves an estimated 1,200 internal staff hours (~$100K) or 800 consultant hours (~$260K).
  • The CSOP is approximately 2% of consultant cost or 6% of internal staff cost for equivalent documentation.
  • Delivered same-day. Compare to 9 to 18 months for internal development or 6 to 12 months for a consultant.
Enterprise Procedures

What Is The Cybersecurity Standardized Operating Procedures (CSOP)?

The Cybersecurity Standardized Operating Procedures (CSOP) has complete coverage for the Secure Controls Framework (SCF). The SCRP / SCF version of the CSOP is an enterprise-class solution for cybersecurity procedures, and it contains a catalog of over 1,500 editable procedure statements that come in both Word and Excel format, so you have the flexibility to import the procedure statements into a tool (e.g., GRC platform) or edit in Word. The CSOP is a one-time purchases with no software to install - you are buying Microsoft Office-based documentation templates that you can edit for your specific needs. If you can use Microsoft Office or OpenOffice, you can use this product!

The structure of the SCRP / SCF maps to over 200 statutory, regulatory and contractual frameworks, so the CSOP is the most comprehensive set of procedures that you will find for the price.

  • The CSOP addresses the “how?” questions in an audit, since procedures provide the means for how your organization's policies and standards are actually implemented.
  • The CSOP provides the underlying cybersecurity procedures that must be documented, as may be stipulated by statutory, regulatory and contractual requirements.
  • The procedure statements in the CSOP can be cut & pasted into other tools (e.g., wiki page) or left in a single document. There is no wrong answer for how procedures are maintained, since every organization is unique in the tools used and the location of users.

Given the difficult nature of writing templated procedure statements, we aimed for approximately an "80% solution" since it is impossible to write a 100% complete cookie cutter procedure statement that can be equally applied across multiple organizations. What this means is ComplianceForge did the heavy lifting and you just need to fine-tune the procedure with the specifics that only you would know to make it applicable to your organization. It is pretty much filling in the blanks and following the helpful guidance that we provide to identify the who / what / when / where / why / how to make it complete.
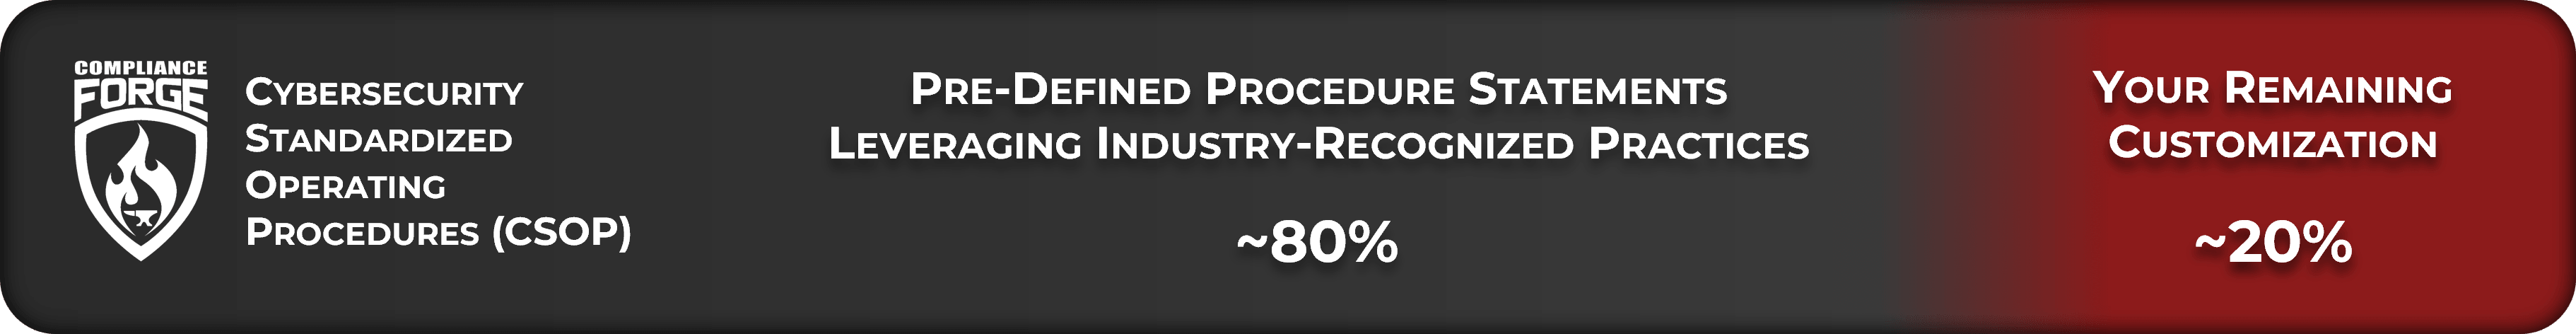
ComplianceForge CSOP Cybersecurity Procedure Template Customization
What Problems Are There?

What Problem Does The CSOP Solve?

Lack of In House Security Experience
Writing cybersecurity procedures is a skill that most cybersecurity professionals simply are not proficient at and avoid the task at all cost. Tasking your security analysts and engineers to write comprehensive procedure documentation means you are actively taking them away from protecting and defending your network, which is not a wise use of their time. The CSOP is an efficient method to obtain comprehensive IT security procedures for your organization!
Compliance Requirements
Nearly every organization, regardless of industry, is required to have formally-documented security procedures. Requirements range from PCI DSS to HIPAA to NIST 800-171. The CSOPis designed with compliance in mind, since it focuses on leading security frameworks to address reasonably-expected security requirements.
Audit Failures
Security documentation does not age gracefully like a fine wine. Outdated documentation leads to gaps that expose organizations to audit failures and system compromises. The CSOP's procedures provide mapping to leading security frameworks to show you exactly what is required to both stay secure and compliant.  
Vendor Requirements
It is very common for clients and partners to request evidence of a security program and this includes the procedures.

Our customers choose the Cybersecurity Standardized Operating Procedures (CSOP) because they:

  • Have a need for comprehensive cybersecurity procedures to address their compliance needs.
  • Need to be able to edit the document to their specific technology, staffing and other considerations.
  • Have documentation that is directly linked to leading frameworks (e.g., CMMC, NIST CSF 2.0, NIST 800-53, NIST 800-171, ISO 27002, HIPAA and others).
  • Need an affordable and timely solution to address not having procedures.
How Solutions Does It Provide?

How Does The CSOP Solve These Problems?

Clear Documentation

The CSOP provides a comprehensive template for your procedures to help prove that your security program exists. This equates to a time saving of hundreds of hours and tens of thousands of dollars in staff and consultant expenses!

Time Savings

The CSOP can provide your organization with a templated solution that requires minimal resources to fine tune for your organization's specific procedural needs.

Alignment With Leading Practices

The CSOP is written to support over two dozen leading frameworks!

Until now, developing a template to provide worthwhile cybersecurity procedures is somewhat of a "missing link" within the cybersecurity documentation industry. The good news is that ComplianceForge solved this issue with the Cybersecurity Standardized Operating Procedures (CSOP) product. We are the only provider to have an affordable and comprehensive procedures template! Our CSOP can save a business several hundred hours of work in developing control activities / procedure statements, so the CSOP is worth checking out!

Common Questions

Frequently-Asked Questions

Here are answers to common questions about the SCF procedures template:

How many procedure statements are in the SCF procedures template?
The SCF procedures template contains more than 1,500 editable procedure statements. Each statement maps 1-1 to a Secure Controls Framework control, so the procedures cover the full SCF. ComplianceForge sells it as the SCF version of the Cybersecurity Standardized Operating Procedures (CSOP), and we wrote it to answer the "how" questions auditors ask after they've reviewed your policies and standards.
Do the SCF procedures line up with the SCRP policies and standards?
Yes, both are mapped 1-1 to Secure Controls Framework (SCF) controls, so they line up control by control. ComplianceForge's SCRP policies cover each SCF domain and its standards cover each SCF control, while each procedure statement in the SCF version of our CSOP also maps to an SCF control. That shared mapping lets your team trace a requirement from the policy, to the standard, to the procedure that shows how the control is performed, which answers the "how" questions raised in an audit.
How much customization does an SCF procedures template need?
An SCF procedures template still needs tailoring to each organization's technology, staffing and processes, because templated procedures cannot apply universally. The structure and wording are already written, so most of the work is fine-tuning each procedure with details only the organization knows, such as its technology, staffing, system names and responsible roles. That is far less effort than writing more than 1,500 procedure statements from a blank page.
How long does it take to write cybersecurity procedures from scratch?
Writing a full set of cybersecurity procedures from scratch usually takes many months. Internal development typically runs 9 to 18 months, and consultant work 6 to 12 months, which equals roughly 1,200 internal staff hours or 800 consultant hours. By comparison, ComplianceForge delivers the SCF version of the Cybersecurity Standardized Operating Procedures (CSOP) the same day you purchase it, so your time goes into customizing procedures rather than drafting them.
Can SCF procedures be imported into a GRC tool or wiki?
Yes, because the SCF procedures template comes in Word and Excel formats, procedure statements can be kept in a single document, pasted into a wiki, or imported into a GRC platform. It is a one-time purchase with no software to install. Each procedure statement stays tied to its SCF control, which preserves traceability after the content moves into another tool.