Short answer: NIS2 is the updated European Union (EU) Network and Information Systems (NIS) Directive and requires in-scope organizations to adopt documented cybersecurity risk-management measures, approved and overseen by management. You do not need a separate NIS2 policy library. Build one hierarchy of policies, standards and procedures mapped to a common control set such as the Secure Controls Framework (SCF), then show how each NIS2 measure traces to it, alongside ISO 27001 and other obligations.
NIS2 matters to more organizations than many expect. In its threat landscape report published, ENISA states that "73% of the targeted organisations are essential and important entities as per the NIS2 definition," and that it "still observed the targeting of cyber dependencies, including supply-chain attacks and third-party attacks." For organizations in scope, documentation is the evidence that risk-management measures exist and are governed.
NIS2 (Directive (EU) 2022/2555) is implemented through national laws in each EU member state, so the exact obligations depend on where you operate. At the directive level:
Article 21 measures translate into documents, where each requirement must trace to a policy, a standard with measurable requirements and at least one procedure:
Many organizations subject to NIS2 likely utilize ISO 27001, customer security questionnaires, GDPR and sometimes US frameworks. Writing a separate policy set for each one creates conflicting statements and multiplies maintenance. A single hierarchy mapped to a common control set avoids that. The Secure Controls Framework maps its controls to more than 200 laws, regulations and frameworks, and the SCF lists the NIS2 Directive among them. When your standards map to SCF controls, one statement can satisfy the matching NIS2 measure, the ISO 27001 Annex A control and other requirements at the same time.
The Hierarchical Cybersecurity Governance Framework keeps that set usable:
That structure also makes it easier for management bodies to approve policies without wading through procedural detail.
ComplianceForge's premium GRC content provides SCF-aligned policies, standards and procedures designed for import into a GRC platform, and the ISO 27001 / 27002 policies and standards serve organizations that prefer ISO structure.
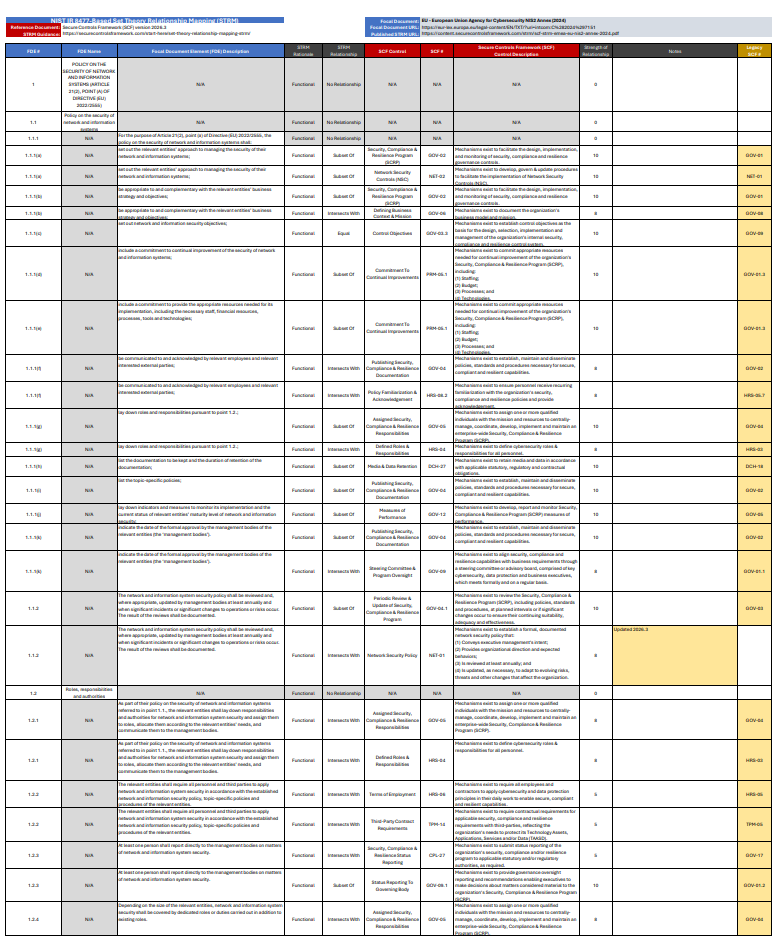
Any NIS2 journey should start with reading the requirements and performing a crosswalk mapping to your existing documentation structure. The SCF uses Set Theory Relationship Mapping (STRM) to perform crosswalk mappings and this provides evidence of reasonable practices used to identify and implement applicable capabilities:
The NIS2 directive describes risk-management measures rather than a fixed document list. Documented policies, standards and procedures are the practical way to show those measures exist and are approved by management.
No. ISO 27001 covers much of the same ground, but NIS2 adds obligations such as management accountability and incident reporting. Map both to a common control set to see the gaps.
Article 20 places responsibility on the management bodies of in-scope entities to approve and oversee the measures.
Yes, if the policies map to a common control set such as the SCF, which crosswalks to both EU and US requirements.
