
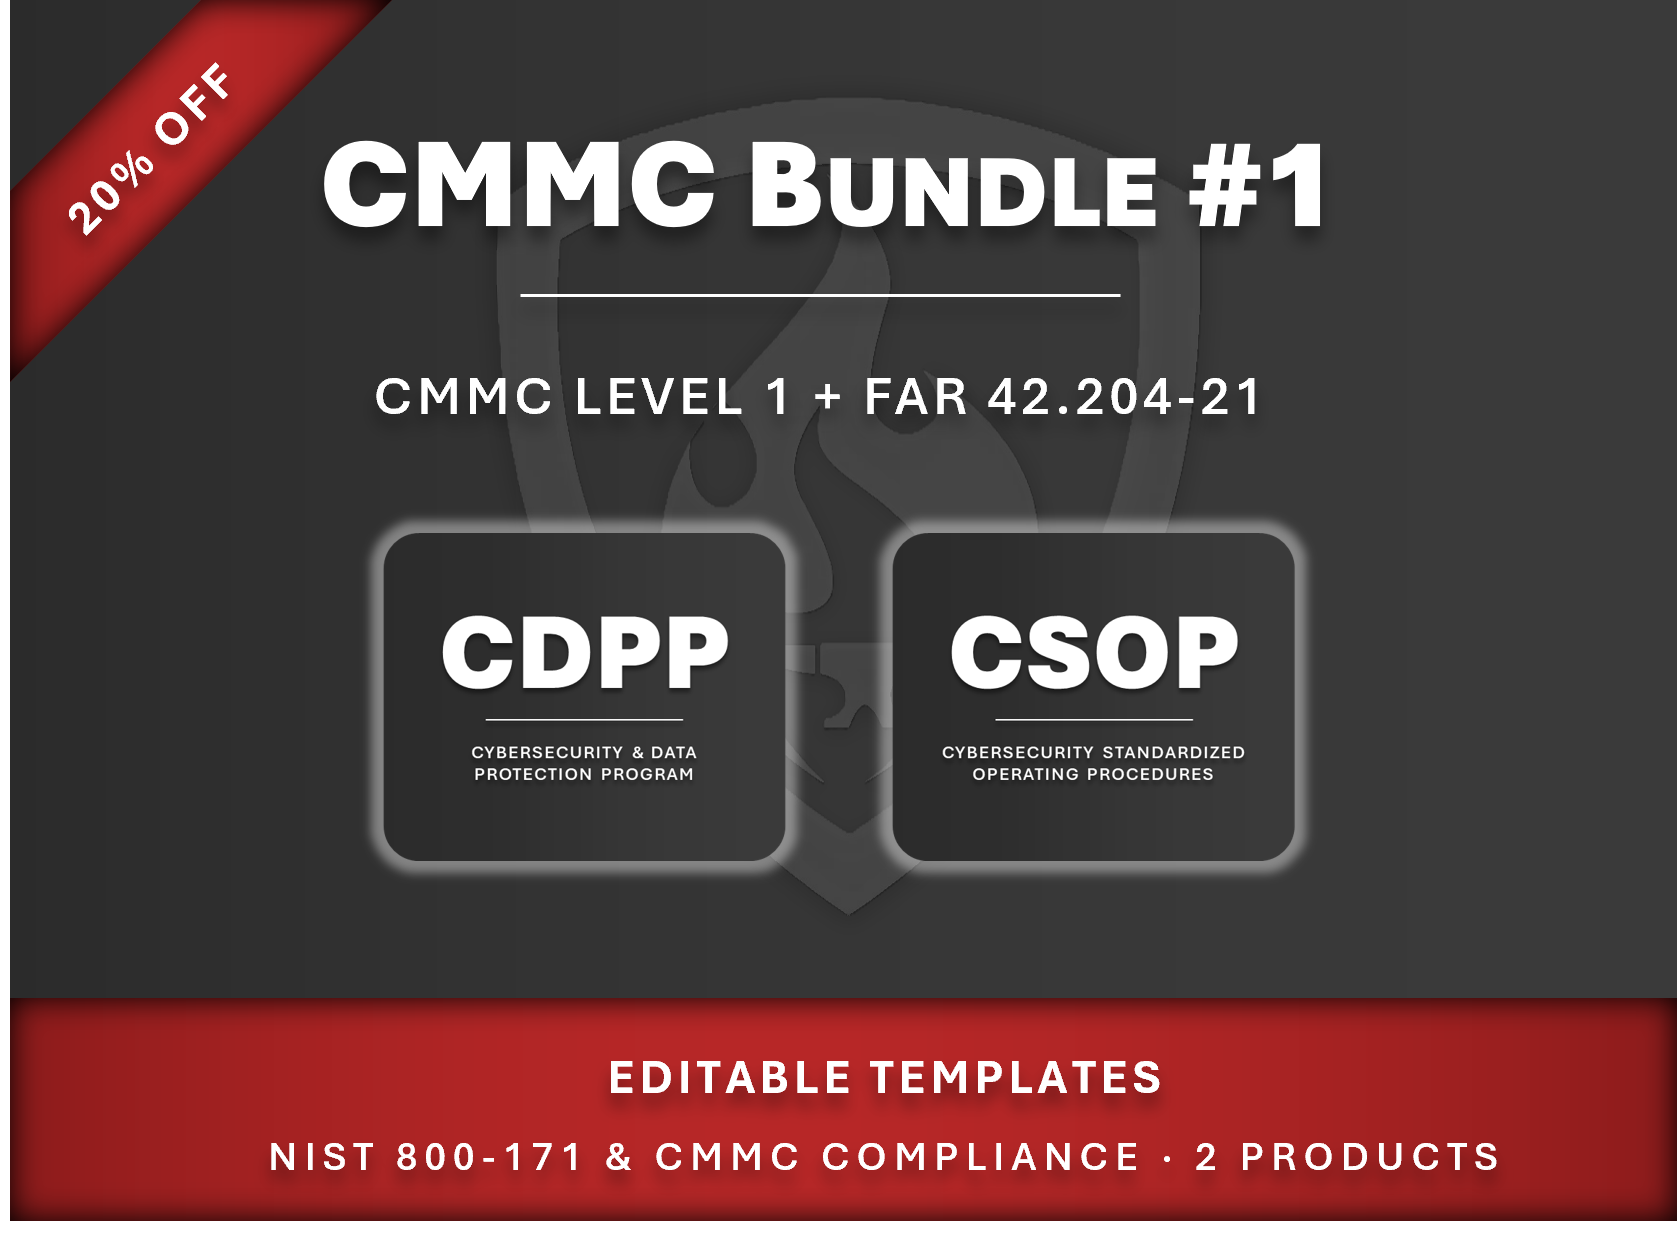
- Four CMMC bundles cover the spectrum from CMMC 2.0 Level 1 (FAR 52.204-21) through Level 3 (highest-sensitivity CUI).
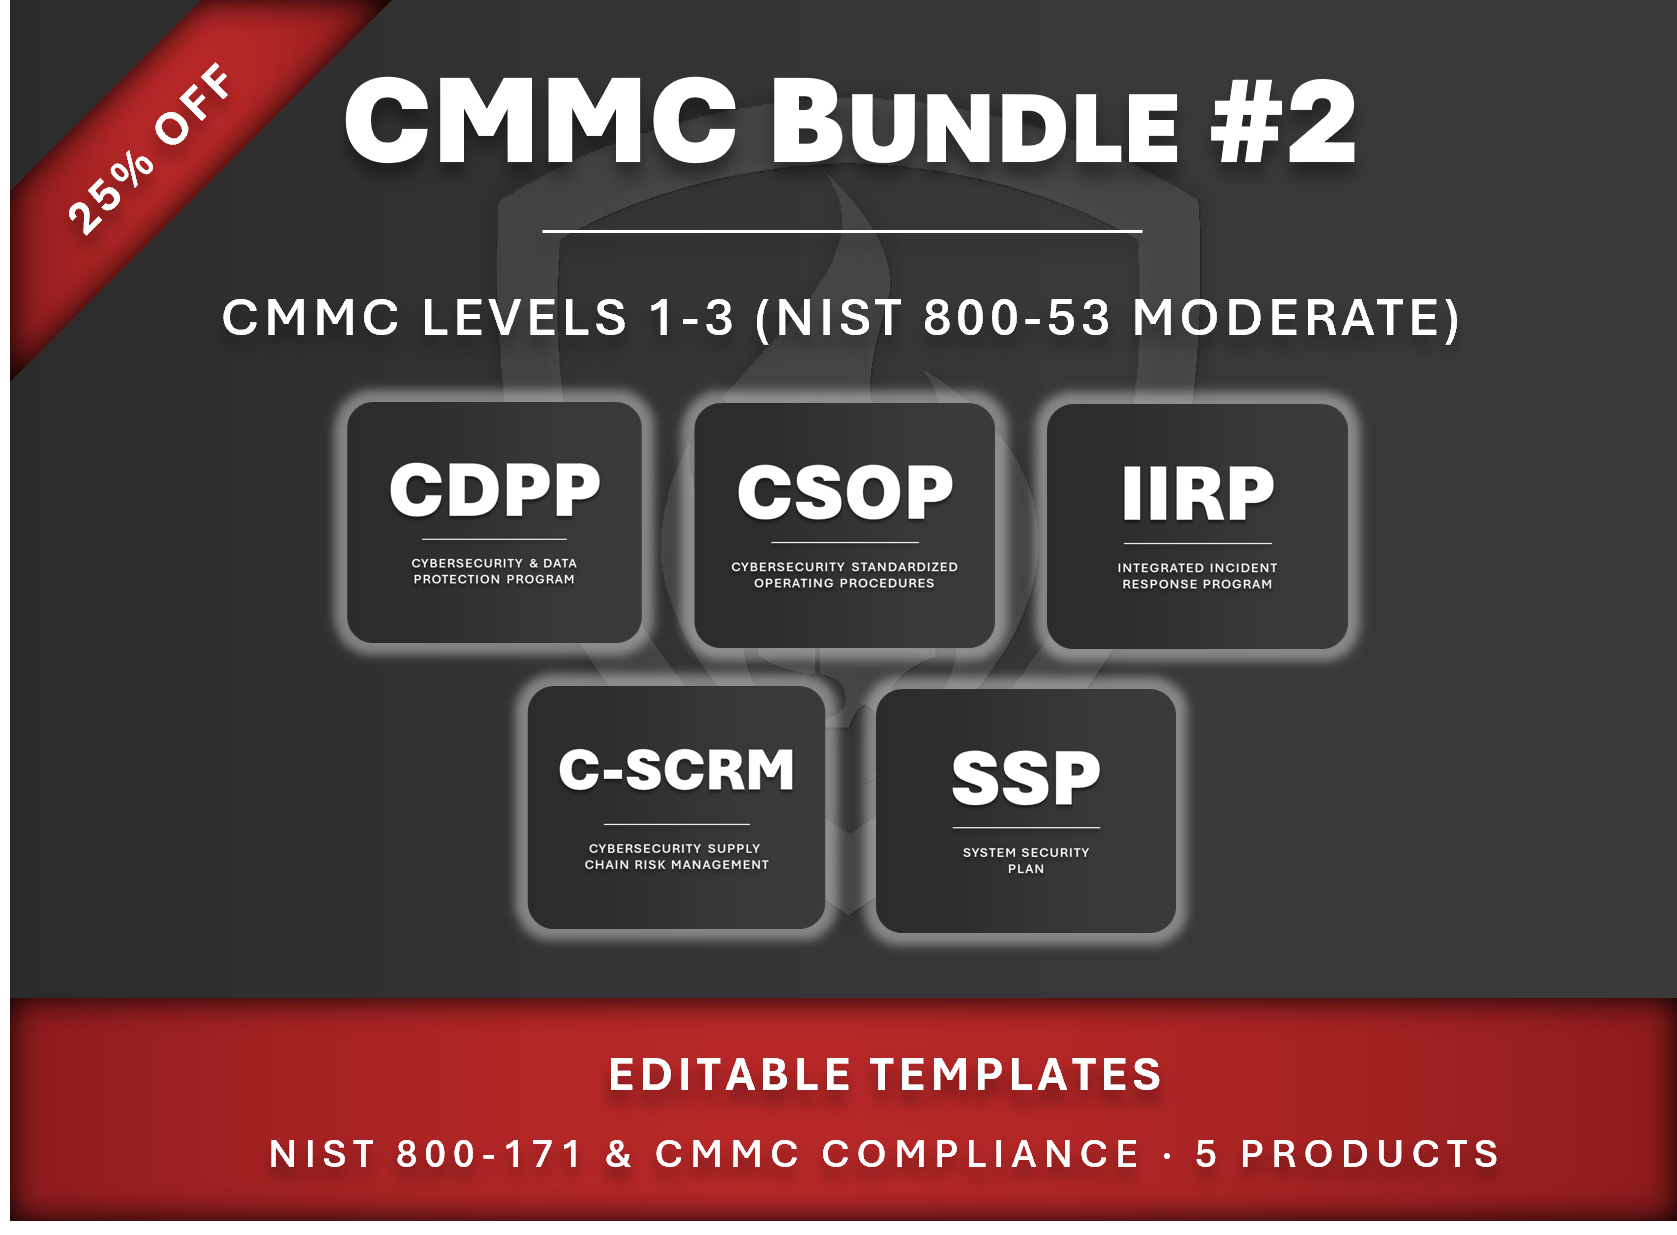
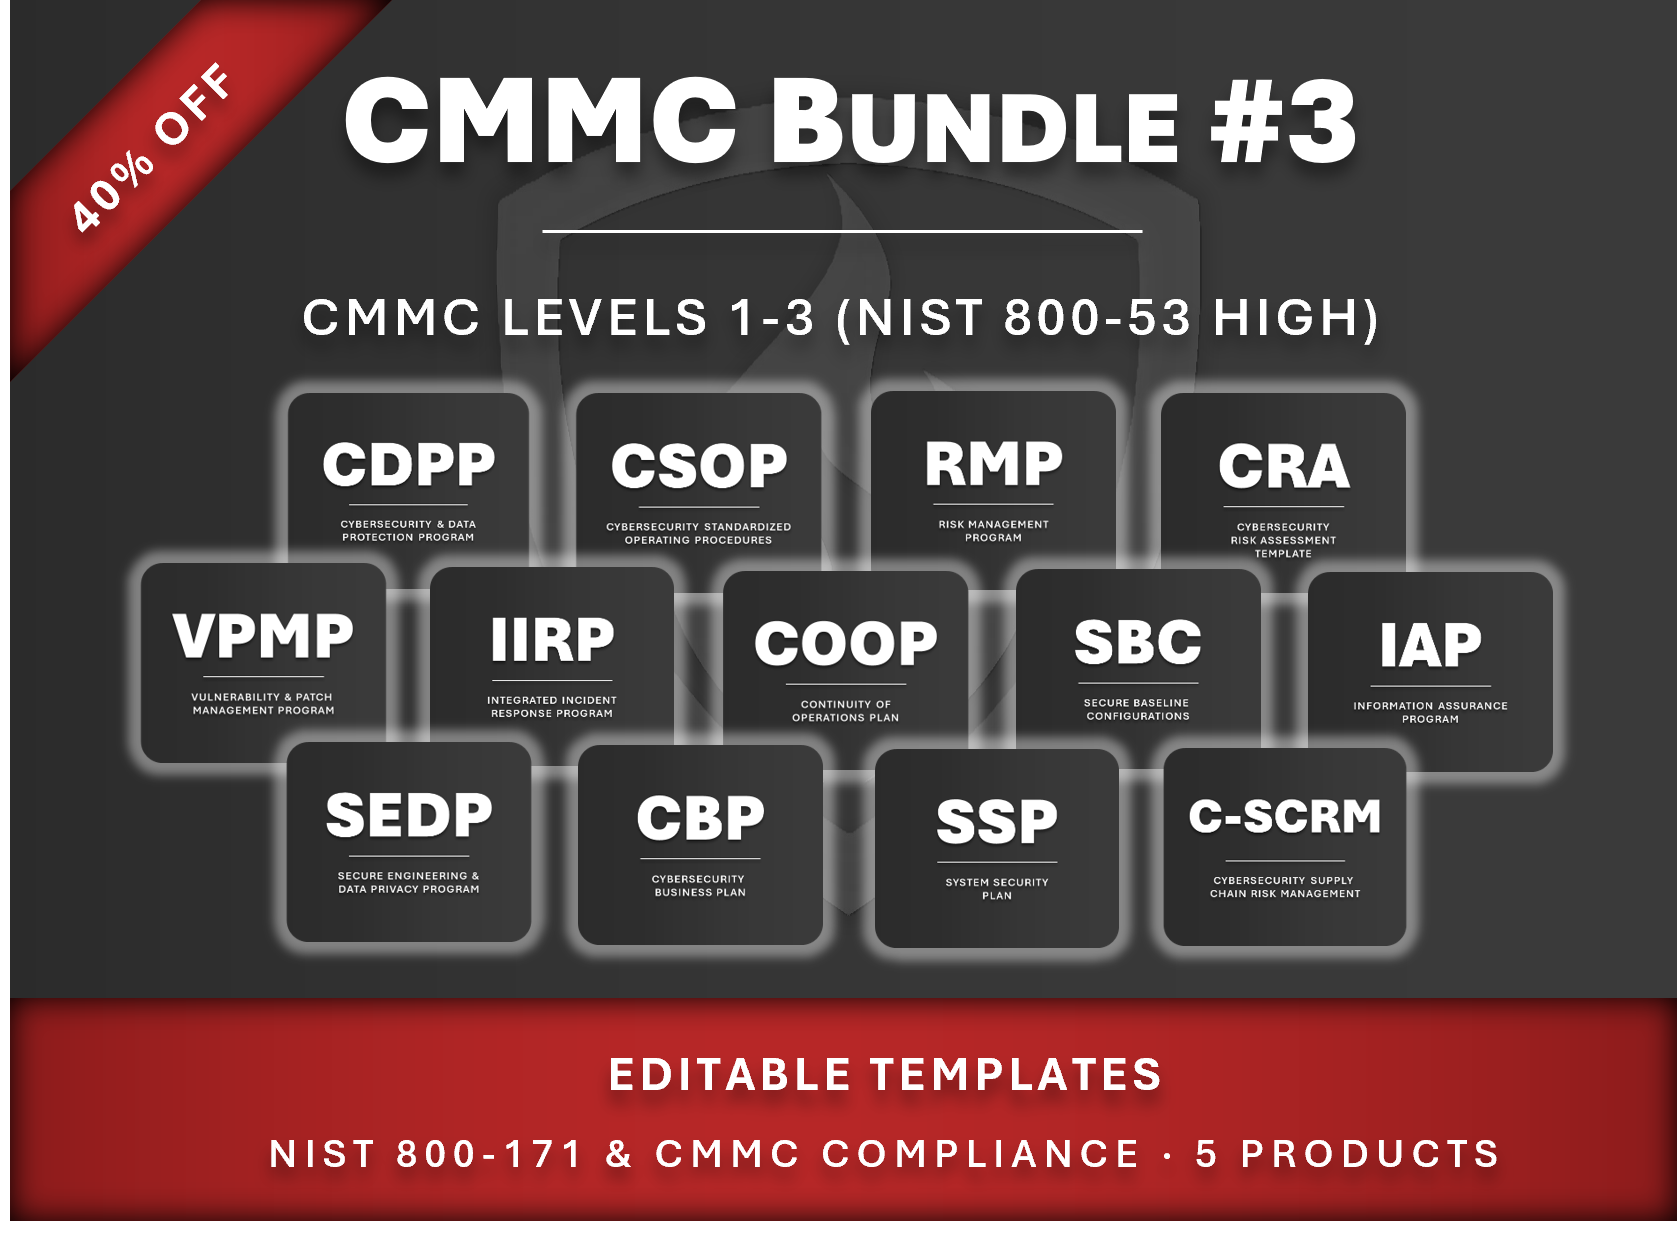
- Bundle 1 is FAR 52.204-21 / Level 1 focused. Bundles 2-4 cover Levels 1-2 or Levels 1-3 with different framework alignments.
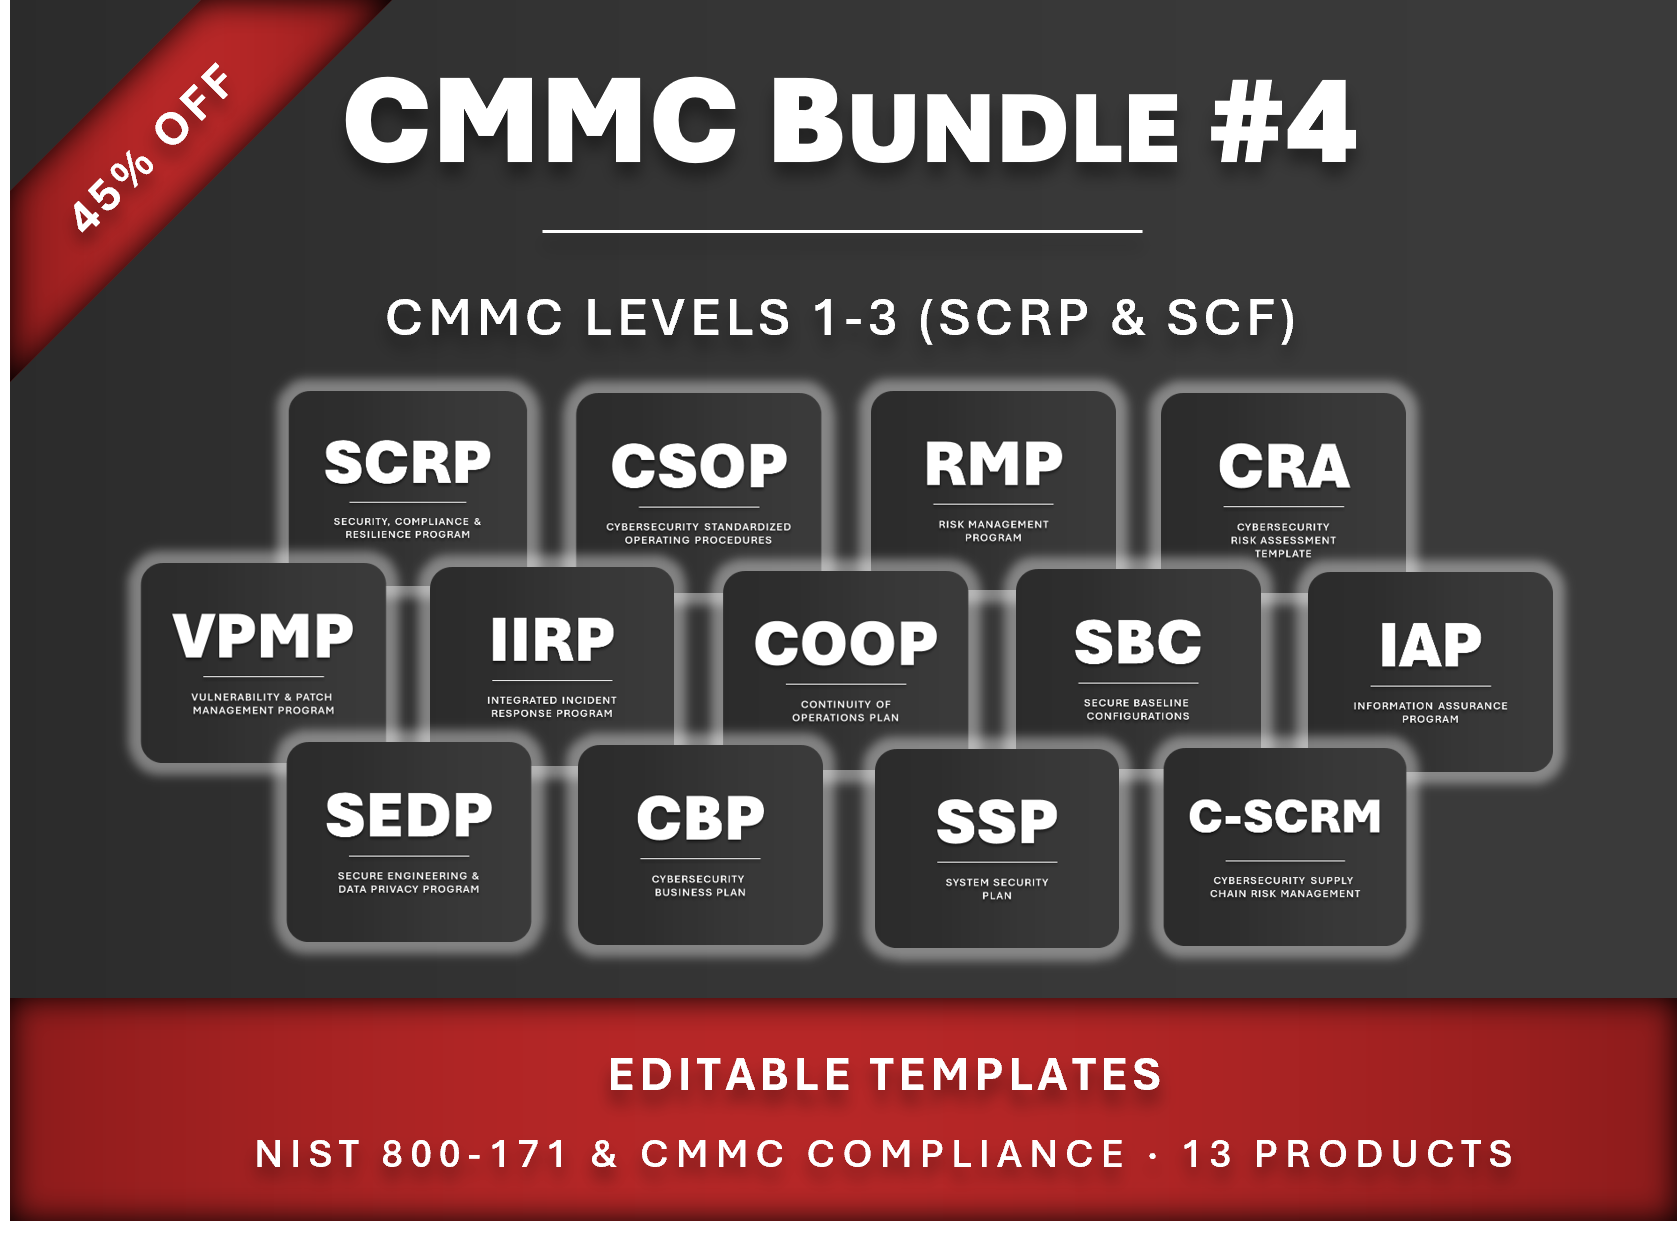
- Bundle 2 aligns with NIST 800-53 Moderate. Bundle 3 aligns with NIST 800-53 High. Bundle 4 aligns with the SCRP/SCF for maximum framework coverage.
- Discounts range from 20% to 45% versus individual product pricing. Bundle 4 (SCF-aligned) offers the largest discount.
- All bundles include DIBCAC battle-tested documentation that has been used successfully in third-party assessments.
NIST 800-171 & CMMC Solutions
ComplianceForge's NIST 800-171 & CMMC solutions are comprehensive and span the policies, standards, procedures, System Security Plan (SSP), Plan of Action & Milestones (POA&M), third-party risk management and other documentation that businesses need demonstrate compliance. The documentation is written with no blanks to fill out and is ready for your organization-specific customization:
- The policy statements are ready to be adopted, requiring little to no editing.
- The standards are targeted at approximately 90-95% complete, since it is expected that there will be some customization (e.g., unique password strength requirements or organization-specific Bring Your Own Device (BYOD) requirements).
- The procedures are targeted at approximately 75-80% complete, since there is such a variety of technologies and resources. We’ve done the heavy lifting and your subject matter experts just have to fill in the details.
- We have quite a few options for NIST 800-171 & CMMC compliance efforts. It really depends on the focus of your compliance efforts, if you just need to comply with NIST 800-171 & CMMC or if you have other compliance obligations that you need to address.
Comprehensive Coverage for NIST 800-171 Compliance Requirements
As a quick summary of your requirements to comply with NIST 800-171, you are expected to have several different types of documentation to prove that your cybersecurity program exists. The reality with compliance assessments is that if something is not documented, you cannot prove it exists. Given that reality, you need to ensure your company has the following cybersecurity documentation in place:
- Cybersecurity policies, standards & procedures;
- System Security Plan (SSP) (requirement #3.12.4); and
- Plan of Action & Milestones (POA&M) (requirements #3.12.1, 3.12.2, 3.12.3 & 3.12.4)
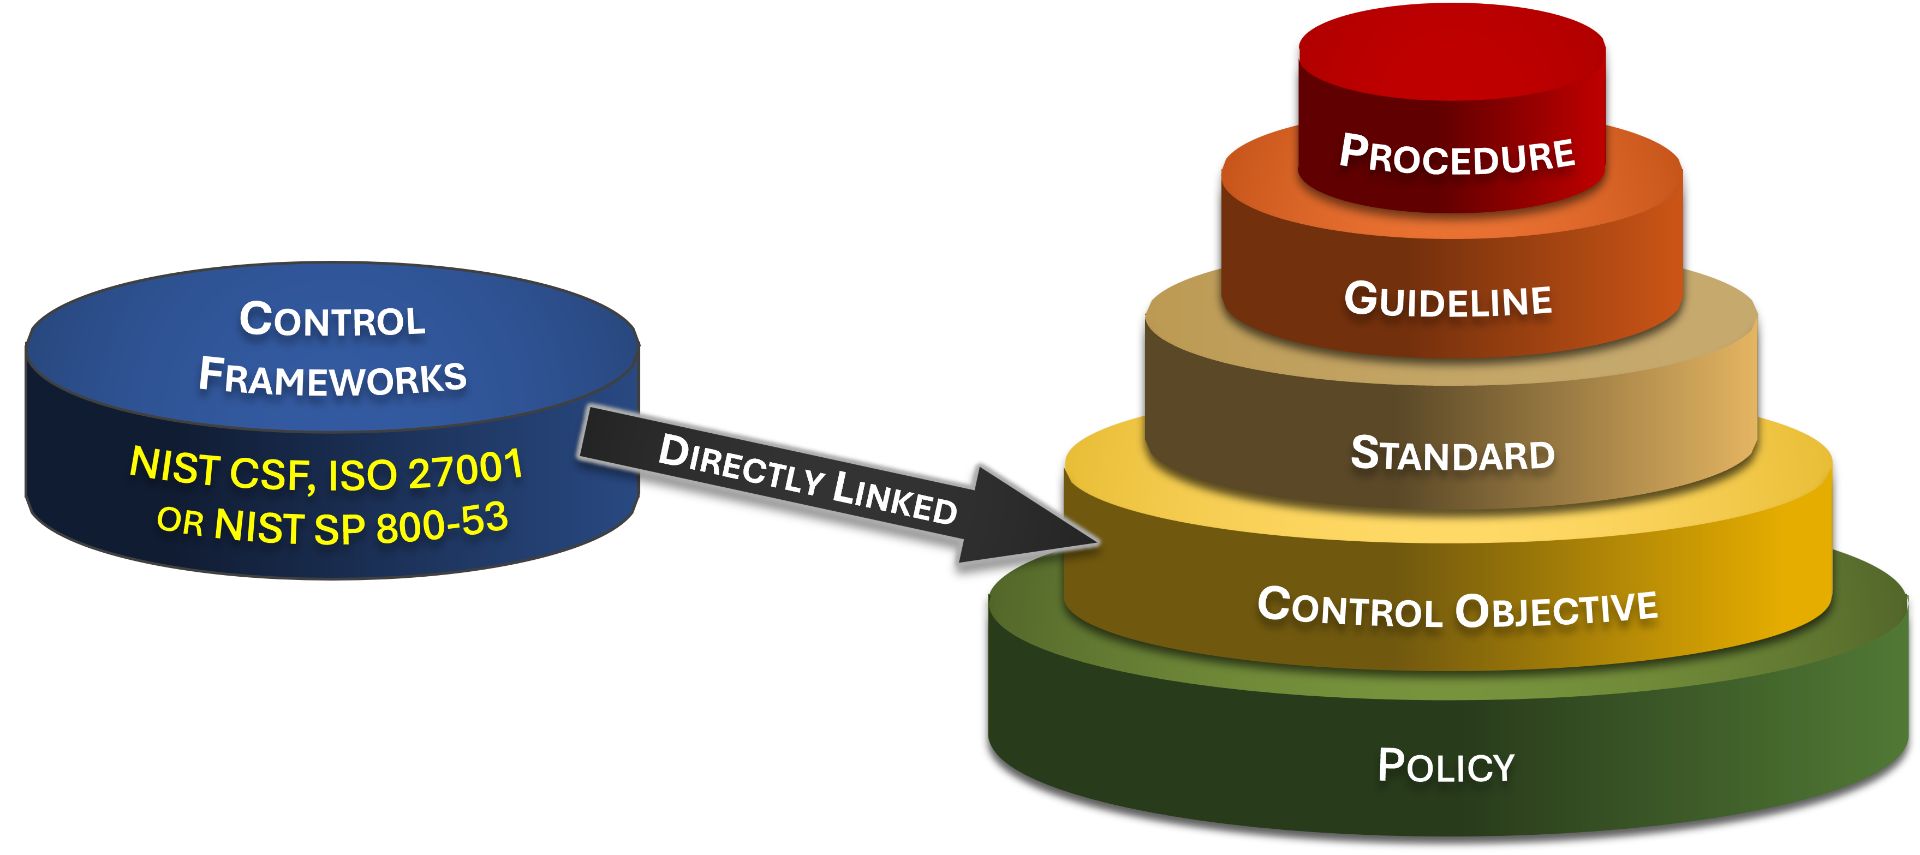
NIST 800-171 & CMMC Compliance Documentation - Policies, Standards, Procedures and more!
In the downloadable CMMC requirements mapping matrix shown below, you can see how all CMMC 2.0 Levels 1, 2 & 3 requirements are supported by ComplianceForge products.
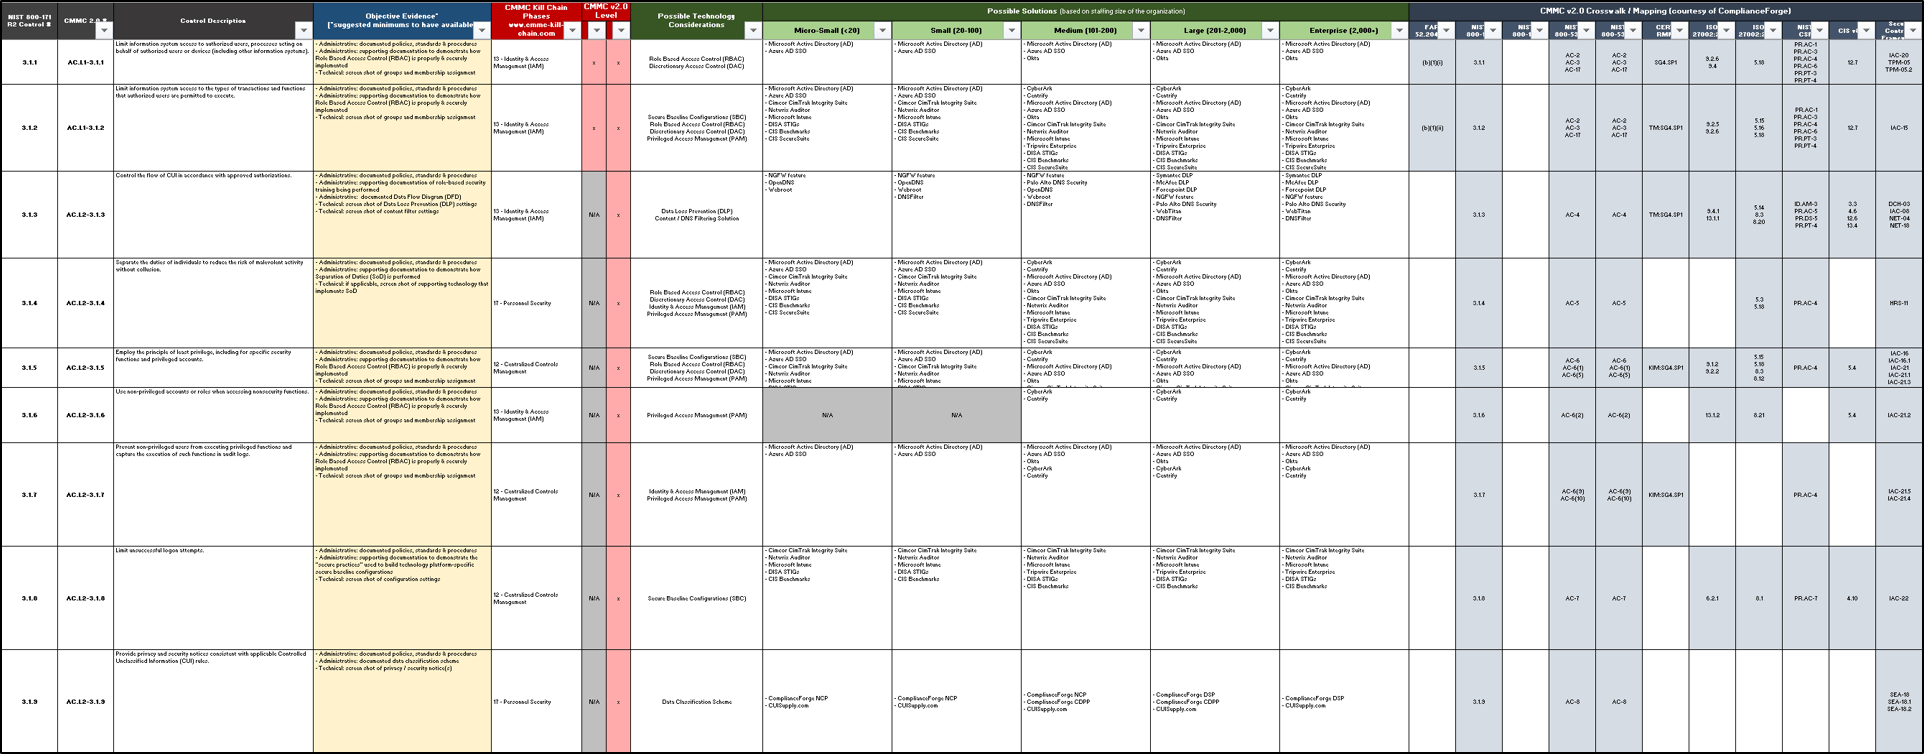
NIST 800-171 & CMMC Compliance Documentation - Policies, Standards, Procedures and more!
In the downloadable CMMC requirements mapping matrix shown below, you can see how all CMMC 2.0 Levels 1, 2 & 3 requirements are supported by ComplianceForge products.
DIBCAC Battle-Tested Documentation
When it comes to NIST 800-171 & CMMC compliance, ComplianceForge's editable policies, standards, procedures and other templates are a business accelerator - our products can save you time and significantly reduce the labor costs that are traditionally associated with researching and developing NIST 800-171 & CMMC policies, standards and procedures on your own or by hiring a consultant to do it for you. These are not "fill in the blanks" templates - while they are expected to be edited for your specific needs, these policies, standards and procedures templates are written to address leading secure practices. ComplianceForge documentation can be scoped to address multiple environments (e.g., on-premises and/or in a hosted environment).
ComplianceForge’s NIST 800-171 / CMMC documentation has been used successfully by multiple companies during DIBCAC assessments to efficiently and effectively generate the necessary artifact documentation to demonstrate compliance with NIST SP 800-171 controls and NIST SP 800-171A control objectives. This battle tested documentation includes the necessary policies, standards, procedures, SSP, POA&M, Incident Response Plan (IRP) and other documentation that are expected to exist to successfully pass a third-party assessment, be it DIBCAC or a C3PAO.
What About NIST 800-171 Rev 3 Changes?
NIST SP 800-171 Rev 3 was published on May 14, 2024 and replaced Rev 2, which NIST withdrew the same day. Rev 3 has 97 security requirements in 17 families, assessed through 510 assessment objectives in NIST SP 800-171A Rev 3. DoD contracts and CMMC Level 2 still reference Rev 2 today (see the current Rev 2 vs Rev 3 status), and ComplianceForge's NIST 800-171 documentation supports both revisions. Browse all 97 NIST 800-171 Rev 3 requirements, or see what changed at the assessment objective level in the NIST 800-171 R2 to R3 Transition Guide.
In its change analysis for the final SP 800-171 Rev 3, NIST reported the following changes from Rev 2:
Note: NIST's change-type counts add up to 98 rather than 97. Its change analysis marks the withdrawn Rev 2 requirement 3.13.2 as both a minor change and a withdrawn requirement, so 14 of the 97 final Rev 3 requirements are minor changes.
How Do ComplianceForge Products Apply To NIST 800-171 Compliance?
Complying with the requirements from DFARS goes beyond just having policies and standards. When you break down the requirements to comply with DFARS / NIST 800-171, you will see how ComplianceForge's products address a specific DFARS compliance need.

In the chart, "NFO" stands for Non-Federal Organization. NFO controls are required for contractors and are called out in Appendix E of NIST 800-171.
Security, Compliance & Resilience Program (SCRP)
252.204-7012
NIST 800-171 (multiple NFO controls)
252.204-7012
NIST 800-171 NFO PS-7
252.204-7012
NIST 800-171 NFO RA-1
252.204-7012
NIST 800-171 3.11.1
252.204-7012
NIST 800-171 3.11.2
252.204-7009
252.204-7010
252.204-7012
NIST 800-171 3.6.1
252.204-7012
NIST 800-171 NFO SA-3
252.204-7012
NIST 800-171 3.12.4
252.204-7012
NIST 800-171 (multiple NFO controls)
252.204-7012
NIST 800-171 3.6.1
252.204-7012
NIST 800-171 3.4.1
252.204-7012
NIST 800-171 NFO CA-1
One of the most important things to keep in mind with procedures is that the "ownership" is different than that of policies and standards:
- Policies, standards and controls are designed to be centrally-managed at the corporate level (e.g., governance, risk & compliance team, CISO, etc.).
- Controls are assigned to stakeholders, based on applicable statutory, regulatory and contractual obligations.
- Procedures are by their very nature de-centralized, where control implementation at the team-level is defined to explain how the control is addressed (e.g., network team, desktop support, HR, procurement, etc.).
Given this approach to how documentation is structured, based on "ownership" of the documentation components:
- Policies, standards and controls are expected to be published for anyone within the organization to have access to, since it applies organization-wide. This may be centrally-managed by a GRC/IRM platform or published as a PDF on a file share, since they are relatively static with infrequent changes.
- Procedures are "living documents" that require frequent updates based on changes to technologies and staffing. Procedures are often documented in "team share" repositories, such as a wiki, SharePoint page, workflow management tool, etc.

Available CMMC Product
Outside of the bundles, we have an individual product designed to help comply with NIST 800-171 Rev 2 and Rev 3 called the NIST 800-171 Compliance Program (NCP). If your compliance requirements do not require additional documentation which our other products provide, this may be the solution for you.
Available CMMC Bundles
Going beyond the NCP, we provide four bundles covering CMMC 2.0 from Level 1 through Level 3, and each bundle has a different framework foundation and discount percentage.
Comprehensive Coverage
Give us a call or send us an email - we are happy to help you find the right solution for your needs!
There are a lot of choices to pick from when selecting a cybersecurity framework. If you are not sure what works best for you, you can read more here. The most common frameworks are NIST 800-53, ISO 27002, the NIST Cybersecurity Framework and the Secure Controls Framework (SCF). To do NIST CSF, ISO 27002 or NIST SP 800-53 properly, it takes more than just a set of policies and standards. While those are foundational to building a cybersecurity program aligned with that framework, there is a need for program-specific guidance that helps operationalize those policies and standards (e.g., risk management program, third-party management, vulnerability management, etc.). It is important to understand what is required to comply with NIST CSF vs ISO 27002 vs NIST SP 800-53, since there are significantly different levels of expectation.
It is important to understand that picking a cybersecurity framework is more of a business decision and less of a technical decision. Realistically, the process of selecting a cybersecurity framework must be driven by a fundamental understanding of what your organization needs to comply with from a statutory, regulatory and contractual perspective, since that understanding establishes the minimum set of requirements necessary to:
- Not be considered negligent with reasonable expectations for cybersecurity & data protection;
- Comply with applicable laws, regulations and contractual obligations; and
- Implement the proper controls to secure your systems, applications and processes from reasonable threats, based on your specific business case and industry practices.
This understanding makes it easy to determine where on the "framework spectrum" (shown above) you need to focus for selecting a set of cybersecurity principles to follow. This process generally leads to selecting the NIST Cybersecurity Framework, ISO 27002, NIST SP 800-53 or SCF as a starting point.
Frequently Asked Questions (FAQs)
Here are answers to common questions about NIST 800-171 and CMMC bundles: